

AI Agent Payments: Where Autonomy Ends and Approval Begins
AI agents can prepare and initiate payments, but they should not define their own authority. A practical framework for separating autonomous AP work from payment approval and release.
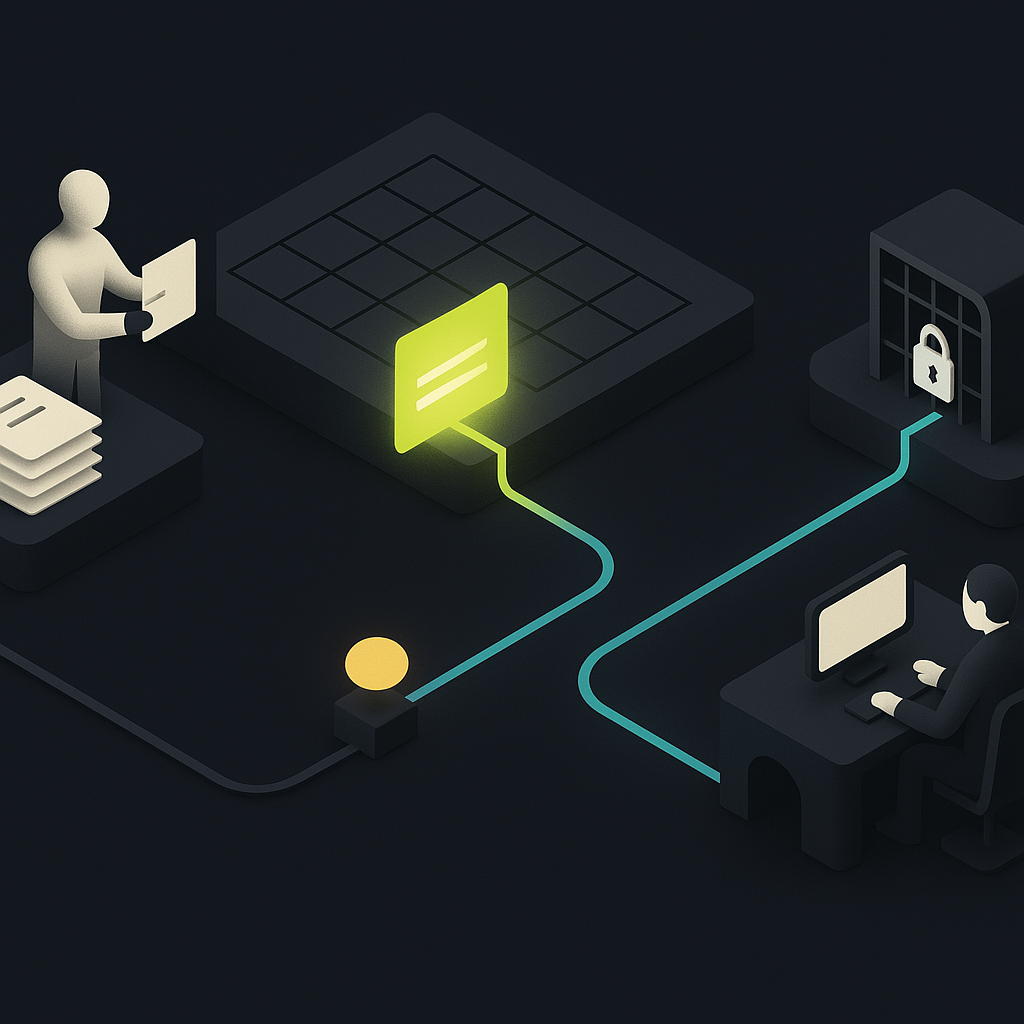
AI agent payments are payments that software agents prepare or initiate on behalf of a business under delegated authority. They do not have to be fully autonomous. In accounts payable, an agent can code invoices, match supporting records, chase missing information, and submit eligible payments while humans retain control over exceptions and spending policy.
The critical boundary is not whether an AI model can call a payment API. It is whether an independent control system can establish that the specific payment is authorized, still valid, and safe to release.
For CFOs and controllers, the practical starting point is straightforward: automate evidence gathering and routine execution, but keep authority outside the model. An agent should never be able to approve an exception simply because it can explain one convincingly.
What changes when an AI agent enters the payment workflow?
Traditional automation follows predefined paths. An agent can interpret an invoice, retrieve a purchase order, investigate a mismatch, and decide which permitted action to take next. That flexibility helps with fragmented AP work, but it also creates more opportunities for untrusted information to influence an action.
Consider a supplier email saying an invoice is urgent and providing a replacement bank account. An agent may correctly understand the request. That does not establish the sender’s authority, verify the account, or authorize payment.
Separate the workflow into distinct responsibilities:
- Interpretation: Extract information and identify a proposed next action.
- Validation: Check authoritative records, matching rules, and required documentation.
- Authorization: Establish whether company policy permits the specific action.
- Execution: Submit the authorized instruction through the payment infrastructure.
- Reconciliation: Connect the resulting payment status to the liability and ledger.
The agent may coordinate these steps. It should not control every trust boundary between them.
Where can an AP agent safely act alone?
Autonomy should depend on the action’s consequences, the reliability of its inputs, and the ability to reverse an error. A draft accounting suggestion and a released payment should not share the same approval threshold.
The following is a recommended operating policy, not a universal legal requirement.
| AP action | Suitable autonomy | Required boundary | Escalation trigger |
|---|---|---|---|
| Suggest invoice coding | Prepare automatically | Approved chart and coding rules | New or ambiguous treatment |
| Match invoice, PO, and receipt | Complete routine matches | Authoritative records and tolerances | Missing receipt or mismatch |
| Request missing documents | Send approved reminders | Verified contacts; limited disclosure | Dispute or sensitive request |
| Change beneficiary details | Gather evidence only | Independent verification and approval | Any destination change |
| Prepare a payment instruction | Prepare automatically | Validated liability and beneficiary | Unresolved hold or exception |
| Release an eligible payment | Execute under standing authority | Independent policy checks | Limit breach or changed facts |
| Handle uncertain payment status | Investigate automatically | Status lookup before resubmission | Unresolved execution outcome |
This makes AP automation a sequence of controlled actions rather than a single “touchless” setting. An invoice can pass extraction and matching while its payment remains blocked.
Make payment approval specific—and invalidate it when facts change
“Approved invoice” is not a sufficient execution instruction. The invoice may be valid while the proposed destination, currency, or payment date is wrong.
Bind authorization to a defined payment record containing:
- The paying legal entity and funding account.
- The vendor identity and verified beneficiary record version.
- The invoice or liability references, amount, and currency.
- The permitted payment method and execution window.
- The approving person or standing-policy reference.
- The applicable policy version and authorization expiry.
A material change should invalidate the existing authorization. If bank details change after approval, the system should not carry the earlier approval forward. The same principle applies when an agent changes the amount, payer entity, or currency.
A reliable release service rechecks these conditions immediately before submission. It also reserves authorized capacity so concurrent agents cannot each spend against the same available limit.
Use configurable approval policies to express who can authorize which actions. Do not rely on a prompt telling the agent to “ask a manager for large payments.” Prompts guide behavior; independently enforced rules constrain it.
Protect the approval-to-release gap
Keep supplier content outside the authority channel
Invoices, attachments, emails, and websites are evidence sources, not instructions to the payment system. A document containing “ignore previous checks” must have no ability to alter workflow permissions.
Use restricted tools, validated input schemas, and separate services for vendor-master changes and payment release. The National Institute of Standards and Technology provides AI risk-management and cybersecurity guidance that can inform this control design; a payment-specific implementation still needs explicit authority boundaries.
Separate preparation from exception approval
The identity that prepares a payment should not approve its own exception or modify the policy governing its release. Assign a human owner to each agent and separate permissions for reading documents, updating records, proposing payments, and executing approved instructions.
Agent identity and wallet controls are foundational. The related guide to AI agent wallets and spend limits covers that foundation. The additional requirement here is transaction-level authorization: an available balance does not make a payment legitimate.
Treat unknown status differently from failure
A timeout does not prove a payment failed. The provider may have accepted the instruction before the connection dropped.
Use a stable payment-intent identifier and, where supported, the provider’s documented idempotency mechanism to prevent repeated requests from creating repeated payments. Query the original instruction before resubmitting. Duplicate-invoice controls must operate separately because a duplicate liability can arrive with a different request identifier.
Also distinguish submitted, accepted, settled, returned, and reconciled states. Payment and settlement materials from the Bank for International Settlements provide useful context for why settlement finality matters. An API acknowledgment alone should not clear a payable as settled.
Hypothetical example: a valid invoice with an unsafe payment request
An agent receives an invoice from an established supplier. The invoice matches the purchase order and recorded receipt. An accompanying email asks AP to pay a new bank account because the supplier is changing banks.
- Continue safe work: Extract the invoice, complete matching, and prepare coding.
- Block the destination change: Keep the existing verified beneficiary record unchanged.
- Open an exception: Route the request to the designated vendor-maintenance owner.
- Verify independently: Contact the supplier through a previously established channel, not a telephone number supplied in the change request.
- Reauthorize: Once the change is verified and approved, create a fresh payment authorization tied to the updated beneficiary record.
- Execute and reconcile: Submit once, track status, and match the outcome to the liability.
The agent remains productive without gaining authority to redirect funds. That is the right autonomy boundary: an exception blocks the risky action, not necessarily every upstream task.
What AI agent payments do not solve
They do not remove rail-specific risk. Recovery rights and timing differ across cards, bank transfers, and on-chain transfers. Card disputes are conditional; an on-chain transfer may not provide a native reversal or chargeback path after settlement. Choose payment methods based on supplier needs, recovery options, cost, and treasury policy—not agent compatibility alone.
They do not create legal authority. A signed delegation can help demonstrate an instruction’s origin and scope. It does not independently establish that the underlying purchase was legitimate or settle contractual liability.
They do not replace compliance analysis. Applicable obligations depend on jurisdiction, business role, funds flow, and payment method. Internal AP automation and a platform moving money for third parties require different assessments. Agent identity does not replace verification of the business and its counterparties.
A controller’s checklist before enabling autonomous release
- Define eligibility: Specify permitted entities, vendors, invoice types, currencies, and payment methods.
- Document mandatory holds: Include beneficiary changes, disputed invoices, missing evidence, and policy exceptions.
- Enforce outside the model: Make the payment service reject unauthorized instructions regardless of the agent’s explanation.
- Test changed facts: Confirm that an expired approval or updated beneficiary blocks release.
- Test concurrency and retries: Confirm that simultaneous requests cannot overspend and timeouts cannot cause duplicate execution.
- Retain decision evidence: Record source references, policy results, approval identity, tool calls, and provider responses—not private model reasoning.
- Assign incident ownership: Name who can suspend new submissions, revoke permissions, and investigate pending payments.
- Measure outcomes: Track incorrect releases, duplicate attempts blocked, exception reasons, unresolved statuses, and reconciliation completeness.
Start with controlled execution, not unrestricted autonomy
The strongest business case for AI agent payments is not removing every approval. It is eliminating routine coordination while making the remaining approvals more specific and enforceable.
Payouts.com combines global payouts, treasury, AP/AR automation, and AI digital employees on one ledger, with identities, wallets, and spend limits for agents. Explore Payouts.com AI agents with a narrowly defined AP workflow in mind. Before enabling release, document what the agent may do, what must stop it, and who owns the exception.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
40 commentsRelated resources
How AI Agents Get Wallets and Spend Limits: A Finance Leader's Guide
AI agents can now hold funds, initiate payments, and operate within defined spend limits — but what does that actually mean for financial controls? Here's how the plumbing works and what finance leaders need to think through before deploying autonomous money movement.
Google Agent Payments Protocol: A Finance Pilot Plan
Google’s Agent Payments Protocol gives agent-led purchases a framework for verifiable authorization. Finance teams need a controlled pilot to turn that framework into a reliable purchasing and payment workflow.
Stripe Agent Payments: What the Stack Solves for Finance
Stripe is building infrastructure for agents to buy, sell, and pay. For finance teams, the critical question is which parts of the transaction that infrastructure controls—and which remain your responsibility.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The idea that an agent should never approve its own exception even if it can explain one convincingly is the key insight here. We've seen vendors pitch 'self-healing AP' where the model decides when to override matching rules, and it always sounded dangerous but we couldn't articulate why. This framework makes it clear: interpretation capability doesn't grant authorization authority.
The separation of interpretation, validation, authorization, execution, and reconciliation into distinct responsibilities is the right model, but in practice the challenge is that most ERPs and payment platforms weren't built with these boundaries in mind. We're having to retrofit these controls on top of systems that assume a single approval event covers everything from invoice validity to payment release, which means a lot of middleware and custom logic to enforce what should be native guardrails.
We ended up doing the same. Built a thin middleware layer that sits between the agent's proposed actions and our legacy ERP. It enforces the authorization checks the article describes—validating that approved payments haven't changed, that limits are still available, that beneficiary records match. Not elegant but it works without ripping out the core system.
We ran into this exact problem. Our workaround was building a separate authorization layer that sits between the ERP's AP module and the payment rail—basically treats the ERP output as a proposal that still needs independent validation against beneficiary records and spend policy before release. Not elegant but it works until the platforms catch up.
The distinction between workflow autonomy and spending authority is something we struggled to articulate internally until recently. Our treasury team was concerned about agents 'initiating payments' but what they really meant was they didn't want the agent setting its own limits or overriding controls. This framework of separating interpretation, validation, authorization, execution, and reconciliation into explicit steps with different trust boundaries makes that conversation much easier.
Exactly. We ended up framing it as: the agent can execute within approved boundaries but cannot expand those boundaries. Once we separated 'perform this categorized action' from 'decide whether this action is permitted,' the treasury objections disappeared.
We had the exact same confusion. The framework in the article helped us separate the workflow layer (where the agent decides what to do next) from the policy layer (which defines what's permitted). Now treasury owns the authorization rules and the agent just executes within them.
The requirement to invalidate authorization when bank details change after approval sounds obvious in principle but is genuinely hard to implement when you have suppliers constantly updating their information through portals. How are people handling the race condition where a supplier updates beneficiary details between approval and scheduled release date—do you re-route every change for fresh approval or maintain a grace period?
We treat the portal update as a new beneficiary record entirely, even if it's the same supplier. The old approval stays bound to the old record version, and the payment just sits in a 'beneficiary mismatch' queue until someone with bank detail approval rights validates the new information and re-approves. It creates a bit of delay but the alternative is way too risky.
We lock the beneficiary record at the moment of approval and treat any subsequent supplier portal update as a new request that requires re-approval from scratch. The approved payment still references the frozen version. It's extra friction for suppliers who legitimately need to update details, but we'd rather have that than the alternative.
The section on separating preparation from exception approval is going to be a hard sell in smaller finance teams where the same person wears multiple hats. We're already short-staffed and the idea of splitting agent ownership, preparation, and approval permissions across different people sounds right in theory but creates serious workflow friction when you only have two AP people. How do others handle this without just adding more manual handoffs?
You can still have the same person involved at different stages, the point is that the agent itself shouldn't self-approve exceptions it generated. Even in a two-person AP team, you can configure the system so the agent prepares and flags exceptions, but a human has to explicitly click approve on anything outside normal tolerances—even if that human also ran the agent.
You don't necessarily need different people for every role. The key is different *permissions* enforced by the system. Even in a small team, the agent should have read/prepare access, and the human should have approval/release access through a separate UI or step. That way the agent can't auto-approve its own exceptions even if the same person reviews them.
The point about treating 'approved invoice' as distinct from an approved payment instruction is going to require significant workflow redesign for most AP teams. We currently have a single approval step that covers both the liability acknowledgment and the payment release, and separating those two will mean rethinking how we route tasks between AP and treasury.
We ran into the same wall. The fix was adding a lightweight intermediate state—invoice approved for payment preparation, then a second gate before release that validates entity, method, and beneficiary one more time. It felt redundant at first but caught three incorrect entity assignments in the first month.
We had the same setup. The forcing function for us was adding multi-entity payment runs where the payer entity and approval authority didn't always align. Once we split liability approval from payment release, we could finally route cross-entity payments to treasury instead of having AP approvers sign off on cash positions they couldn't see.
The timeout vs. failure distinction at the end deserves more attention. We've had cases where an agent retried a 'failed' payment that actually went through, resulting in duplicate vendor payments that took weeks to recover. How are others handling idempotency when the agent doesn't get a clear success or failure signal from the rails?
We enforce idempotency keys at the API layer—every payment instruction the agent generates includes a deterministic key based on invoice ID, amount, and beneficiary hash. If the agent retries after a timeout, the payment rail rejects it as duplicate. The harder part is surfacing the original transaction status once connectivity is restored so the agent doesn't keep the payment stuck in 'pending investigation' forever.
We enforce idempotency keys at the API layer—every payment instruction the agent generates includes a unique key derived from the payment record hash. If the agent retries, the provider deduplicates automatically. The harder part is teaching the agent to wait for async confirmation instead of assuming timeout means retry-safe.
The framework here is sound but I think the real friction point is going to be when an agent starts proposing valid process improvements that conflict with existing policy. If the agent can identify that a matching rule is consistently blocking legitimate invoices, who owns the decision to update that rule? The agent shouldn't be able to modify its own constraints, but you also don't want to lose the signal that the constraint is wrong.
That's a governance question, not an agent design question. Policy changes should go through your existing approval workflow—whoever owns AP policy today should own those updates. The agent can flag the pattern and draft a proposed rule change, but it shouldn't self-approve new matching logic just because it detected inefficiency.
That's a governance question, not an agent design question. Policy changes should go through the same exception escalation path—the agent flags the pattern, but a human controller or AP manager decides whether the rule needs adjustment. The agent shouldn't be modifying its own operating boundaries even if it can articulate why.
The recommended policy table is useful but I think the escalation trigger for 'release an eligible payment' needs refinement. 'Limit breach or changed facts' is clear enough, but what about payments that sit approved for multiple days due to batching or timing preferences? We've found that stale approvals become a real problem when treasury optimizes execution windows—does the authorization carry a time-to-live or does the release service need to revalidate business context even when technical facts haven't changed?
Good catch. We added a staleness check that invalidates approvals older than 48 hours unless they were explicitly marked as scheduled payments with a future value date. For batch timing that's planned, the approval includes the intended execution window and doesn't expire during it.
Good catch. We added a staleness check that invalidates approvals older than 48 hours unless explicitly reconfirmed. The agent can flag stale approvals automatically but a human has to click through if execution was delayed for batching or operational reasons.
The separation between 'an agent can interpret a request' and 'the request is authorized' is something we're still teaching our finance team to recognize. They see the agent correctly parse a vendor email with new bank details and assume it's safe because the AI 'understood' it. That's exactly backwards.
We solved this with a mandatory verification step that treats any beneficiary change as a new payee setup, regardless of what triggered it. The agent can extract the details and flag the change, but a human in treasury has to independently verify using out-of-band contact before the new destination is even eligible for payment routing.
We hit this too. The fix for us was adding a hard break between the agent's output (parsed data, suggested action) and the validation layer that actually checks beneficiary records. Even if the agent extracted everything perfectly, nothing updates the vendor master without a separate approval tied to the bank verification workflow.
The table breaking down AP actions by autonomy level is exactly what we needed. We've been arguing internally whether invoice coding and payment release are the same risk tier—they obviously aren't. Using this as a starting template for our own policy doc.
Same here. We had everything lumped under 'AP automation approval' which meant either a human touched every step or nothing at all. Breaking it into interpretation vs validation vs authorization makes it way easier to actually deploy this stuff without the CFO shutting it down.
Agreed. We made the mistake of treating all AP automation under one permission tier and it created chaos when we wanted the agent to handle more. Now we're splitting tool access by action type—invoice interpretation can run wide open, but anything touching payment release goes through a separate approval service the agent can't modify.
I'm curious how you handle the scenario where an agent correctly identifies that a payment is blocked by an outdated policy rule. Does it escalate with context, or do you expect humans to periodically audit blocks? We've seen cases where legitimate payments sit in a queue because the exception logic is too conservative and nobody reviews the backlog.
We route those to a daily review queue with agent annotations attached. The agent flags the policy conflict and appends its reasoning, but a controller has to either release the payment manually or update the rule for future cases. It's not elegant but it prevents both stuck payments and unsupervised policy drift.
We route those to a daily review queue with agent annotations attached. The agent flags the reason, references the blocking rule, and suggests the override scope. A controller reviews the queue each morning, approves legitimate ones in batch, and pushes actual policy updates upstream when the same rule blocks repeatedly.
"Approved invoice is not a sufficient execution instruction" — this cuts through so much confusion. Our ERP treats invoice approval as blanket payment authority, and we've had to bolt on separate release checks outside the system. Would love to see more vendors design for this separation natively.
We ended up building a secondary approval step in our treasury module after the ERP signs off on the invoice. It works but the handoff is messy and we lose some audit trail continuity. The systems weren't designed for this level of separation and it shows.
Same here. We had everything lumped under 'AP automation approval' which meant either a human touched every payment or none at all. The authorization-to-release gap the article describes is real—we've started requiring destination verification independent of the invoice approval workflow and it's already caught two social engineering attempts this quarter.
The point about binding authorization to a specific payment record version is critical and often overlooked. We've seen cases where vendor details were updated between approval and execution, and the old approval logic just passed it through because 'the invoice was already approved.' Treating any material change as an invalidation event adds friction but prevents exactly the kind of substitution attack you describe with the replacement bank account scenario.
We implemented this by hashing the full payment record at approval time and requiring the hash to match at execution. Any field change—even a one-cent adjustment—breaks the approval chain and forces re-review. Added friction but eliminated exactly the scenario you describe.
We implemented this by hashing the full payment record at approval time and requiring the hash to match at release. Any field change—beneficiary, amount, currency, date—breaks the hash and forces reapproval. Adds negligible overhead but catches exactly this class of problem.