

Established Common Standards for Cross-Border Payments
Cross-border payments rely on several standards, not one global rulebook. Learn what each standard governs, where local requirements still apply, and how to turn standards into enforceable payment controls.
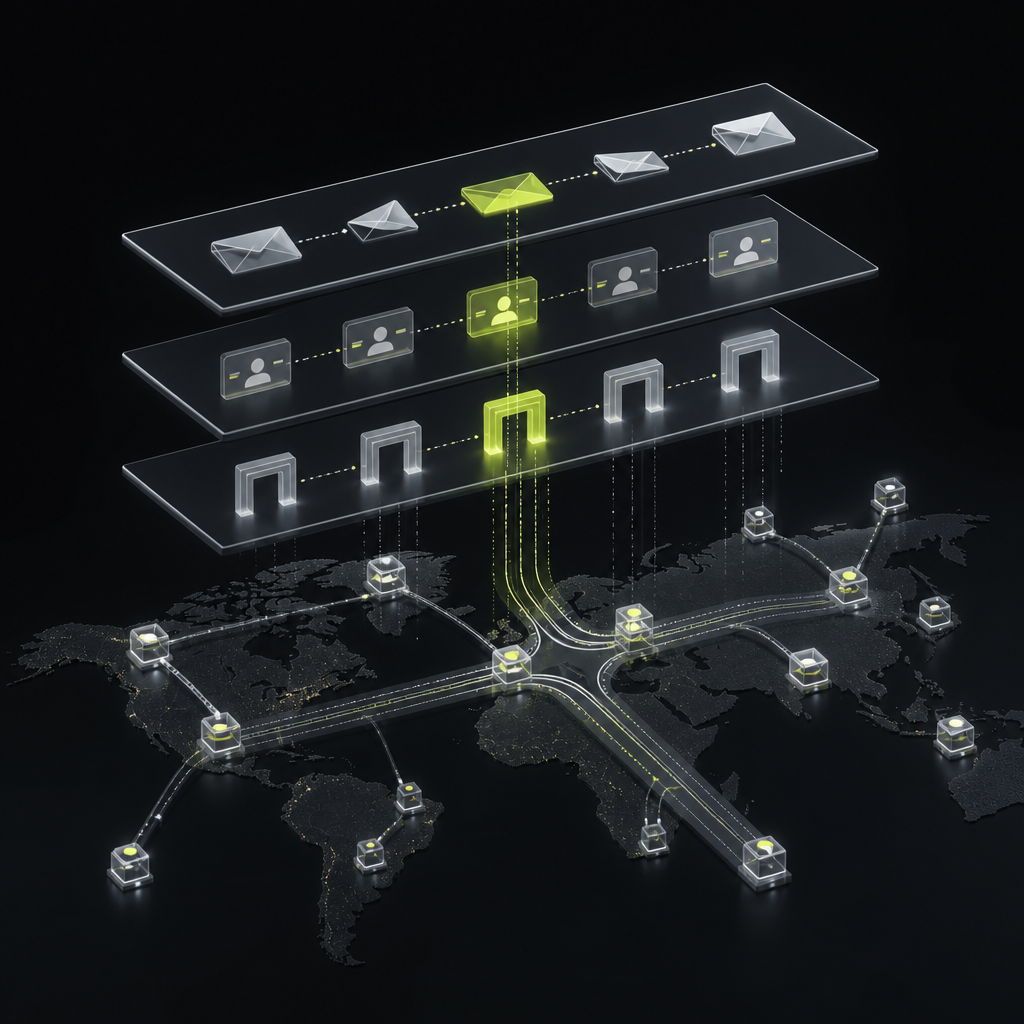
The established common standards for financial transactions in cross border payments include ISO 20022 for financial messaging, BIC and IBAN standards for identification, ISO currency codes, and FATF payment-transparency standards. Network implementation rules, such as Swift’s CBPR+, determine how participants use those standards in practice.
These standards serve different purposes. None creates a universal payment rail, guarantees beneficiary credit, or replaces local law. For finance teams paying vendors, contractors, or sellers internationally, the practical task is to identify which requirements apply to each route—and prove that the payment meets them before release.
The standards stack: what each layer actually governs
“Standards compliant” is incomplete unless the provider identifies the standard, implementation profile, and transaction scope. A payment can use valid identifiers and a valid message format while still failing a receiving bank’s requirements.
| Standard or framework | What it governs | What it does not establish | Operational check |
|---|---|---|---|
| ISO 20022 | Financial message models and definitions | Universal processing or settlement rules | Supported messages and versions |
| Swift CBPR+ | ISO 20022 usage for covered cross-border messaging | Requirements of every domestic rail | Applicable usage guidelines |
| BIC, ISO 9362 | Business party identification | Beneficiary account ownership | Correct institution and routing context |
| IBAN, ISO 13616 | Account identification in participating jurisdictions | Global account-format coverage | Country format and checksum |
| ISO 4217 | Currency identification | FX pricing or account eligibility | Payment and receiving-account currency |
| FATF Recommendation 16 | Payment-transparency expectations | One directly applicable global law | Applicable national implementation |
| CPMI harmonised data requirements | Consistent ISO 20022 data usage | Automatic alignment across providers | Provider mapping and exceptions |
The distinction matters when assigning responsibility. Engineering can validate message structure; payment operations must validate route requirements; compliance must interpret applicable obligations. Passing one check does not substitute for the others.
ISO 20022 is the message language, not the entire payment system
ISO 20022 provides a common model for financial information and message definitions. Its structured fields can distinguish parties, accounts, addresses, and remittance information instead of packing everything into undifferentiated text.
That structure supports automation. A beneficiary name can be screened as a name, while an invoice reference can be used for reconciliation. However, benefits depend on whether participants populate, preserve, and interpret those fields consistently.
Separate the standard from its implementation profile
CBPR+ specifies how ISO 20022 messages are used for covered cross-border payment exchanges on Swift. Swift’s November 2025 migration announcement describes the end of the MT/ISO 20022 coexistence period for cross-border payment instructions on its network. This does not mean every domestic payment system or corporate payment file worldwide now uses an identical format.
Two institutions can both support ISO 20022 but require different fields, message versions, or business rules. A corporate API may also accept a proprietary request format and translate it into a network message downstream.
The CPMI’s harmonised ISO 20022 data requirements address this consistency problem. The operational lesson is straightforward: ask whether providers align data usage, not merely whether they accept an ISO 20022 message.
Test preservation, not just acceptance
A gateway accepting a payment proves only that the request passed that gateway’s checks. Ask what happens when the next system cannot carry the same information:
- Is an address shortened, reformatted, or rejected?
- Does the full remittance reference reach the recipient?
- Are intermediary institutions represented separately?
- Can operations retrieve the submitted data and subsequent transformations?
Silent truncation is particularly dangerous: a technically accepted instruction can still create screening queries or an invoice-matching failure.
Identifiers improve precision without proving identity
BICs identify business parties, commonly financial institutions. IBANs identify accounts using country-specific structures in jurisdictions that use the standard. ISO currency codes make the currency explicit.
These are useful controls, but their limits are important:
- A valid IBAN checksum does not prove ownership. It detects certain structural errors, not whether the account belongs to the intended vendor.
- A BIC is not a beneficiary account number. Identifying the bank does not complete the payment instructions.
- IBAN is not universal. Other destinations require local account and bank or branch identifiers.
- A currency code does not establish receiving capability. An account may not accept the instructed currency, or the receiving institution may convert it.
Collect recipient details conditionally by destination and rail. Do not force every recipient into an IBAN form or assume that a bank identifier alone establishes reachability. The country-by-country contractor payment guide provides a complementary starting point for destination-specific bank details.
Transparency standards and local law are different layers
FATF Recommendation 16 establishes international expectations for information accompanying payments and the responsibilities of institutions in the payment chain. Countries implement FATF standards through their own legal and regulatory frameworks; FATF is not a substitute for jurisdiction-specific compliance analysis.
The FSB’s 2025 consolidated progress report identifies the revision of Recommendation 16 as a milestone in improving payment transparency. Finance teams should distinguish revised international standards from the national rules and provider requirements currently applicable to their transactions.
Avoid turning this into a universal “collect every field” policy. Requirements can vary by transaction type, amount, jurisdiction, and party. Excess collection also increases privacy and security exposure.
Instead, maintain a requirements register that records:
- The field or supporting document required.
- The legal, scheme, or provider basis for the requirement.
- The transactions and jurisdictions to which it applies.
- The effective date and accountable reviewer.
- The access and retention controls for collected information.
Keep tax documentation, customer due diligence, sanctions screening, and payment-message requirements distinguishable. They may use overlapping data, but satisfying one does not automatically satisfy the others.
What common standards do not solve
Standardisation can reduce avoidable data friction. It cannot by itself fund an intermediary account, eliminate FX spreads, extend banking hours, or release a compliance hold.
The FSB’s 2025 assessment of cross-border payment progress reported that policy work had not yet translated into tangible improvements for end users at the global level. It also noted continuing challenges in cost and transparency. This is a reason to measure outcomes separately from standards adoption.
For each payment route, ask for explicit definitions of fees, FX pricing, processing cutoffs, status events, and evidence of beneficiary credit. A standardised message acknowledgement is not necessarily settlement confirmation.
Likewise, choosing between correspondent banking and domestic payout delivery remains a separate routing decision. Use a corridor routing policy to connect data compatibility with cost, timing, and recipient requirements.
Turn standards into a payment acceptance checklist
The most useful operational artifact is a route-level acceptance specification: a documented agreement about required inputs, permitted transformations, status meanings, and exception handling. It should be precise enough for engineering to test and finance to approve.
- Define the route. Record sending entity, destination, payment currency, receiving account type, provider, and delivery rail.
- Identify governing requirements. Separate international standards, network profiles, domestic rules, and provider-specific conditions.
- Specify required data. Record field definitions, conditional requirements, character restrictions, and permitted identifier types.
- Document transformations. Identify where information is mapped, shortened, transliterated, or removed. Escalate changes that alter meaning.
- Define validation boundaries. Distinguish syntax checks from account verification, compliance clearance, and actual delivery.
- Agree on status evidence. Establish what accepted, processing, credited, rejected, and returned mean, including the evidence behind each status.
- Test exceptions. Include missing required information, invalid identifiers, unsupported currency, and downstream rejection. Confirm the repair owner and resubmission controls.
- Control changes. Version requirements, confirm effective dates with providers, and retest affected routes before changing production rules.
Hypothetical example: valid format, incomplete payment
A company submits a supplier payout with a structurally valid IBAN, correct currency code, and an accepted ISO 20022 message. The receiving route also requires a payment-purpose code, which is missing.
The payment is held for repair. Neither the IBAN check nor message acceptance established compliance with that route’s business rules.
The fix is not simply to resubmit. Operations should obtain the appropriate purpose information, update the route’s conditional validation rule, and check whether other queued payments share the omission. Record the failure as a requirements gap rather than a generic bank delay.
Make interoperability an operating requirement
Common standards provide shared language, identifiers, and transparency expectations. Reliable cross-border payouts require an additional layer: route-specific rules, preserved data, clear responsibility, and evidence of payment completion.
Start with an active payout corridor and build its acceptance specification before expanding the approach. When evaluating Payouts.com’s payout automation, bring that specification into the discussion so the conversation focuses on your actual payment requirements—not a generic claim of standards support.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
35 commentsRelated resources
Local Payment Rails vs SWIFT: Build a Corridor Routing Policy
The right payout route depends on the recipient’s currency, bank reachability, funding, and payment purpose—not just the transfer fee. Here is how finance teams can turn that decision into a repeatable corridor routing policy.
How to Pay International Contractors: A Country-by-Country Bank Payment Guide
A successful contractor payment delivers the agreed amount—not just a completed transfer instruction. Build a country-specific payment plan around bank details, currency, fees, and the date funds become available.
Stripe Minimum Payout: Which Threshold Applies to Your Payment?
Stripe does not have one universal minimum payout. Identify the product, currency, and destination first, then separate payment limits from retained balances and platform release policies.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The conditional collection of recipient details by destination is the right call but creates a nightmare for vendor onboarding at scale. We can't realistically maintain different forms for 40+ payout countries, so we end up collecting everything and then validating what's actually required per route. Has anyone found a way to present this to vendors without either confusing them or collecting a bunch of optional fields that never get used?
We took a different approach: single universal intake form that collects the superset, then a validation layer that checks route-specific requirements at payment time. The form is messier but onboarding stays consistent. The tradeoff is we occasionally collect fields we'll never use, but it's better than managing parallel workflows.
We took a different approach: single universal intake form that collects the superset, then route-specific validation runs at submission time and flags what's missing or irrelevant. The form stays consistent but the error messages tell the user what that specific country actually needs. Not perfect but it keeps onboarding from fragmenting across regional teams.
The FATF vs local law distinction is something our compliance team still struggles with. We had assumed that once we mapped fields to Recommendation 16 we were done, but then ran into completely different beneficiary data requirements in Mexico and Malaysia that weren't covered by the FATF framework at all.
Exactly. FATF sets the expectation framework but every jurisdiction implements it differently. We now maintain a matrix that maps FATF Rec 16 elements to actual regulatory requirements by country, and it's shocking how much variation there is in what constitutes sufficient beneficiary information.
Exactly. FATF sets the expectation framework but every jurisdiction implements it differently. We now maintain a matrix that maps FATF Recommendation 16 fields to country-specific regulatory requirements, and it has to be updated quarterly because the local rules keep changing faster than the international standard.
The part about providers needing to specify not just ISO 20022 support but their actual implementation profile is something we now enforce in every contract. After two failed integrations where both sides claimed to be 'ISO 20022 compliant' but couldn't exchange messages without manual mapping, we require vendors to document which CBPR+ usage guidelines they follow, which fields are mandatory vs optional in their implementation, and exactly how they handle unsupported data elements.
We had the same wake-up call. Now our vendor onboarding checklist includes a matrix question: which MT message types are you translating from, which MX versions do you generate, and what happens to optional fields we populate. Saves weeks of troubleshooting later.
The section on testing preservation versus acceptance is critical. We've had several cases where our treasury platform confirmed ISO 20022 submission but the beneficiary's bank received a mangled message with half the remittance data missing. Now we require our providers to document exactly which fields survive the full correspondent chain, not just the first hop.
We do the same now. After getting burned we built a requirement into our RFP process that providers must show field-level transformation logs at each hop in the chain. Most can't actually deliver that, which tells you a lot about how much blind trust we were operating on before.
We do the same now. After getting burned we built a requirement into our RFP process that providers must demonstrate full field mapping at each hop in the chain, not just at submission. The number of providers who couldn't actually show this was shocking.
The stack diagram is helpful but it still doesn't answer the question every AP team actually faces: when a payment fails at an intermediary bank two days after submission, which layer of this stack caused the rejection and who owns the fix? We usually get a generic MT199 or camt.056 with no indication whether it was a format issue, a compliance hold, or a correspondent bank rule we didn't know existed.
We pushed our primary correspondent to define which layer owns each rejection code in their SLA. Turns out about 60% were beneficiary bank format issues that should have been caught pre-flight with proper field mapping. Now we validate against the destination country's domestic requirements before release, not just the correspondent's acceptance criteria.
This is the gap that kills us operationally. We've started requiring providers to commit contractually to structured rejection codes mapped to the article's stack layers, but adoption is mixed. The real issue is that most correspondents still treat rejection reasons as free text, so even when we know which standard failed, the remediation path isn't clear until we escalate.
The statement that a BIC is not a beneficiary account number seems obvious but we still get vendor forms submitted with only the SWIFT code filled in. The article's point about not forcing every recipient into an IBAN form is solid advice but someone needs to explain this to procurement teams who keep sending us standardized forms that literally have one field labeled 'IBAN/Account Number' as if they're interchangeable.
We made the vendor onboarding form conditional based on destination country selection. If the country doesn't use IBAN, those fields don't even appear. Procurement still pushes back because it's "more complicated" than one universal form, but at least we stopped getting blank IBANs for US vendors.
We added a pre-check that flags incomplete bank details before the form even reaches AP. Procurement hated it at first because it added friction, but after explaining that incomplete submissions just bounce back anyway and delay the vendor setup by days, they came around. The real fix was training procurement to understand that payment routing isn't optional metadata.
The distinction between a valid IBAN checksum and actual account ownership is something we had to learn the hard way. We were treating IBAN validation as sufficient verification until a payment went to the correct format but wrong beneficiary—same bank, similar company name. Now we require additional documentary confirmation for new vendors in IBAN countries, which adds friction but has prevented two near-misses since.
We added a beneficiary confirmation workflow after a similar incident. The IBAN validation catches format errors but we now require either a test payment with manual confirmation or a signed letter with account details on company letterhead for any new vendor over a certain threshold. It's friction, but cheaper than the one mistake.
What additional verification layer did you add? We're currently using IBAN validation plus name matching against our vendor master file, but I'm wondering if there's a more reliable intermediate step before we move to full bank account verification services.
The warning about currency codes not establishing receiving capability caught me off guard—we've been assuming that if we send the right ISO code the account can accept it. Has anyone mapped out which correspondent banks auto-convert versus which reject outright? That gap between instructed currency and actual settlement seems like a hidden risk we haven't tracked systematically.
We ran into this exact issue with EUR payments to India. Some intermediaries will auto-convert and charge outrageous spreads, others bounce it back after 3 days. No consistent pattern across banks. The only reliable approach we found was pre-validating with the specific correspondent chain being used, not just the destination account.
We ran into this with GBP to UAE. Our treasury bank auto-converts without notice, while our backup correspondent rejects the instruction entirely and requires AED. The only way we mapped it was by literally sending test payments through each route and documenting the behavior. There's no published matrix that I've found—it varies by institution and sometimes by account type at the same institution.
The point about silent truncation is where we've been burned multiple times. A payment file passes validation, gets accepted by the gateway, then the remittance data gets chopped somewhere downstream and the vendor can't reconcile their invoice. We only find out when they email us three weeks later asking what the payment was for. Would be helpful to know which correspondent banks are the worst offenders for this.
We started capturing the full submitted message and requiring providers to return confirmation of what actually reached the beneficiary bank. It's not perfect but at least we can compare what we sent versus what arrived when these reconciliation issues come up.
We built a post-transmission audit step that pulls the message back from our provider 24 hours later and compares what they actually sent downstream versus what we submitted. Catches truncation before the vendor calls, but it's manual and shouldn't be necessary if providers just documented their field-length limits properly.
The table breaking down what each standard does and does not govern is incredibly useful. We've had multiple incidents where our treasury team assumed CBPR+ compliance meant all downstream banks would handle the payment identically, when in reality each correspondent had different field requirements and truncation rules.
We're seeing the same issue. What helped was mapping field support by correspondent bank upfront and building pre-flight validation that catches mismatches before release. Still manual work to maintain those mappings when banks update their requirements though.
We had the exact same problem. The fix for us was treating CBPR+ as the floor, not the ceiling—then layering route-specific validations on top. Each correspondent bank relationship now has its own documented field mapping and we test it during onboarding, not after the first payment fails.
"Engineering can validate message structure; payment operations must validate route requirements; compliance must interpret applicable obligations." This separation of concerns is exactly right but almost impossible to maintain in practice at smaller companies. We have one person wearing all three hats, and honestly the compliance piece gets shortchanged because no one really knows which national implementation of FATF applies to a Dubai to Singapore payment routed through correspondent banks in two other countries.
Same situation here. We ended up building a shared checklist tied to each payment route that forces all three perspectives into one workflow. Not elegant, but at least nothing gets released until someone has ticked the compliance box, the ops box, and the tech box for that specific corridor.
We solved this by having ops own a decision tree that routes to either engineering (format/API issues) or compliance (screening/documentation) based on the error type. Not perfect but it prevents one person from becoming the bottleneck for every payment hold.
I appreciate the clarification that ISO 20022 migration doesn't mean universal format across all systems. We spent six months last year building to what we thought was the standard only to discover that three of our major banking partners each had different required field sets and validation rules even though they all claimed ISO 20022 support. The CPMI harmonization work can't come soon enough.
This is exactly why the article's point about asking providers to specify their implementation profile matters. We now require banks to document their specific ISO 20022 field requirements during onboarding, not just confirm they support the standard. Saved us from repeating your six-month detour.
Same situation here. We ended up building a shared checklist tied to each payment route that captures both the ISO 20022 base fields and the bank-specific overlays. The question I still can't get a good answer on is whether we should be maintaining separate mappings for each provider or pushing back on them to align to the CPMI harmonized requirements the article mentions.