

Global Payout Platform: Building a Unified Payment Control Layer
A global payout platform should do more than send international payments. It should connect funding, recipient data, execution, and accounting without losing control at the handoffs.
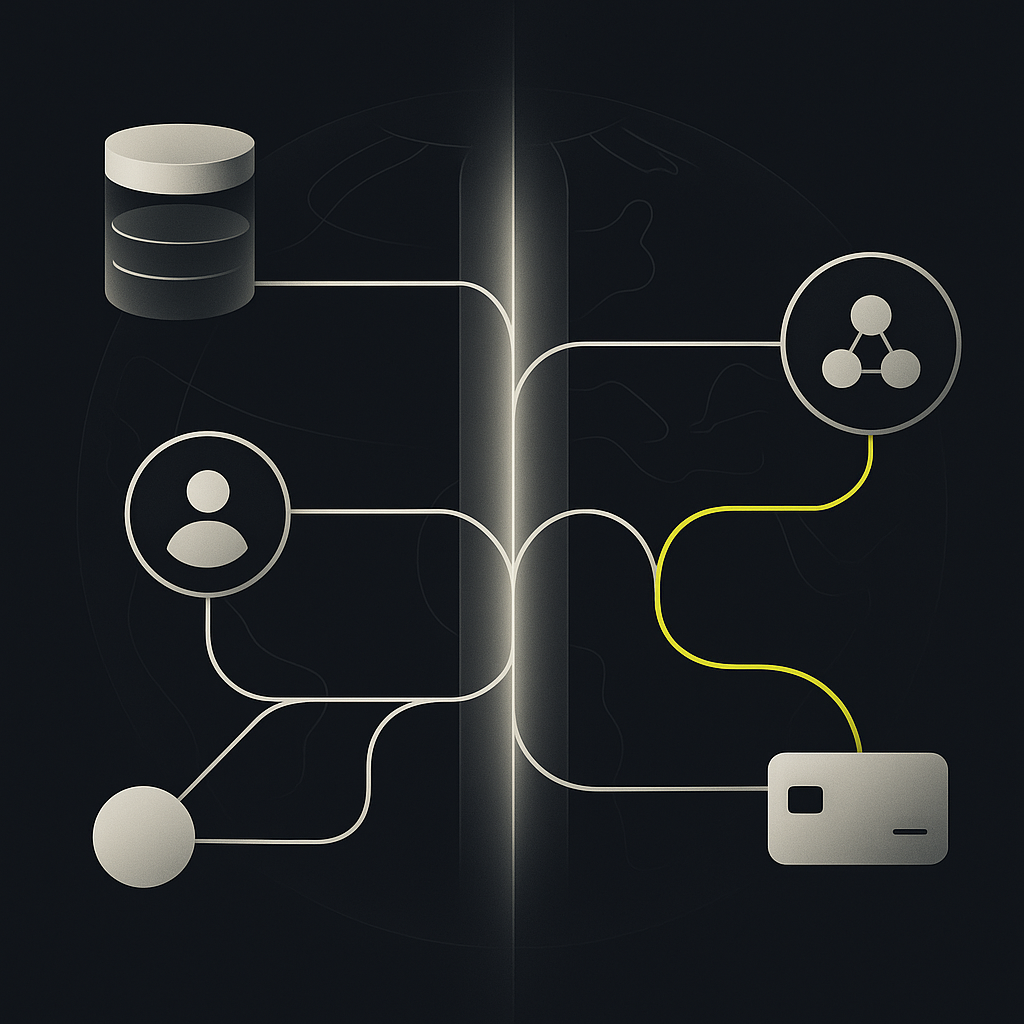
A global payout platform is software and payment infrastructure that lets a business disburse money to recipients across countries through a unified interface or API. Depending on the provider, it can combine recipient onboarding, currency conversion, payment execution, compliance workflows, and reconciliation across bank accounts, cards, or wallets.
For finance teams paying hundreds of international vendors, contractors, or sellers, the strategic value is not simply accessing more destinations. It is maintaining a consistent record of what the business owes, what it has authorized, where the money is, and what remains unresolved.
The right architecture creates a unified payment control layer: shared rules and records across multiple payment providers and rails. It does not make every country work identically. It makes those differences manageable.
What a global payout platform should connect
A bank portal can execute a transfer. An accounts payable system can approve an invoice. An accounting system can record a liability. A global payout platform connects those activities to international delivery, but its exact responsibilities need to be explicit.
Start with an ownership map. Otherwise, a platform may centralize payment submission while leaving funding, exceptions, and accounting scattered across spreadsheets.
| Layer | Platform responsibility to define | Finance control to retain |
|---|---|---|
| Payable intake | Import obligations and source references | Confirm the liability is valid |
| Recipient readiness | Collect and validate route-specific data | Authorize beneficiary changes |
| Funding and FX | Show usable balances and executable quotes | Set liquidity and conversion policies |
| Payment release | Apply approvals and submit instructions | Define limits and segregation of duties |
| Delivery tracking | Normalize statuses and retain evidence | Define when an obligation is discharged |
| Reconciliation | Connect payments, fees, and returns | Approve accounting treatment |
| Exceptions | Surface blockers and route cases | Assign resolution authority |
This division matters because buying payment infrastructure does not transfer every responsibility to the provider. Contract terms, regulated entities, and local partners determine who performs each activity.
Keep one payment identity across the money cycle
The foundational design decision is how records connect. A payable, a payment instruction, and a bank transaction are related objects—not interchangeable ones.
A single payable may require several execution attempts. A batch may generate separate debits for principal and fees. A returned transfer may arrive after the accounting period in which it was sent.
Require the platform to preserve:
- Source obligation ID: the invoice, approved commission, or seller balance being paid.
- Payment instruction ID: the authorized amount, currency, recipient, and destination snapshot.
- Execution attempt ID: each submission to a provider or rail.
- External references: provider and banking identifiers used for tracing.
- Ledger relationships: funding movements, conversion entries, fees, returns, and adjustments.
Use a stable business reference to detect repeat requests, alongside the provider's documented idempotency mechanism. A network timeout must not automatically become a new payment.
When assessing ERP and accounting integrations, ask whether these relationships survive synchronization in both directions. Exporting a completed-payment CSV is not equivalent to maintaining a connected financial record.
Standardize the workflow, not every country's requirements
A common interface should sit above country-specific rules, not replace them. Recipient requirements vary by destination, payout currency, rail, recipient type, and payment purpose.
For example, an Indian bank-account payout commonly requires an account number and IFSC; a UK domestic transfer typically uses an account number and sort code. A Brazilian payout may require CPF or CNPJ information and, depending on the route, bank details or a Pix key. These are examples, not complete submission specifications.
The platform should serve the current field requirements for the selected route, distinguish mandatory from conditional fields, and explain validation failures before release. Format validation alone does not establish account ownership or recipient eligibility.
Compliance also needs a responsibility map. Routefusion's cross-border compliance guide distinguishes business verification, beneficial-owner identification, sanctions screening, and transaction monitoring. These are separate controls, not a single onboarding checkbox.
Document who collects evidence, who evaluates it, who can request more information, and who communicates with the recipient. Store sensitive documentation with appropriate access restrictions rather than copying it into payment notes.
Separate rail access from the delivery promise
Global payout platforms may combine local bank transfers, correspondent banking, card payouts, wallets, and stablecoin infrastructure. Each brings different eligibility, liquidity, and delivery constraints.
As BVNK's discussion of SWIFT alternatives explains, domestic instant systems and alternative networks complement international banking rather than creating one universal replacement. A fast domestic leg does not make funding, conversion, and compliance instantaneous.
Require the platform to distinguish three concepts:
- Available route: the provider supports this destination and payment type.
- Executable payment: funding, recipient data, approvals, and required checks are ready.
- Delivery evidence: the provider has received a defined confirmation from the downstream network.
A status called “completed” is useful only if its meaning is documented. It could describe provider processing rather than confirmed beneficiary credit. Preserve both the normalized platform status and the underlying provider evidence.
Connect payout commitments to usable liquidity
A platform can show a positive balance while a payment remains unfundable. Money may be held in another currency, reserved for another batch, pending settlement, or unavailable to the legal entity making the payment.
The treasury view should separate available, reserved, and in-transit funds by entity and currency. Before releasing a batch, finance needs to know whether its funding requirement includes conversion charges and payment fees.
Multi-currency global accounts can support collecting and holding funds in different currencies. They do not eliminate the need to decide where balances belong or when to convert them. Prefunding improves execution readiness but ties up cash and can leave residual balances in low-volume markets.
Make the FX commitment explicit
Record the currency pair, quoted rate, quote expiry, source debit, recipient amount, and fee allocation. Establish what happens when an approval delay outlasts the quote.
A revised conversion should not silently change an approved recipient amount or exceed a source-currency spending limit. Define when reapproval is required, and disclose whether recipient-side charges can reduce delivery value.
Commercial analysis should include transfer charges, FX margin, funding costs, recipient deductions, return fees, and exception-handling effort—not just the advertised transaction price.
Make exception ownership part of the architecture
Automation often breaks at organizational boundaries. Treasury sees a debit, operations sees a pending status, and accounting sees an unpaid invoice. Without shared references and decision rights, each team can take a different action on the same payment.
Hypothetical example: a timeout after submission
A company submits an approved contractor payment. The API connection times out before returning a result. The platform cannot yet tell whether the provider accepted the instruction.
A controlled workflow marks the attempt as unresolved, queries the provider using the original reference, and prevents an independent resubmission. Operations owns the investigation; treasury sees the potentially committed funds; accounting retains the payable relationship without falsely recording beneficiary credit.
If the provider later confirms acceptance, the platform attaches that evidence to the existing attempt. If it confirms rejection without execution, an authorized retry can proceed. The important control is not an automatic retry button. It is distinguishing an unknown outcome from a confirmed failure.
A practical implementation checklist
Before expanding production volume, establish the following operating rules:
- Name each system of record. Identify where obligations, beneficiary details, approvals, balances, and accounting entries are authoritative.
- Map provider responsibilities. Confirm the contracting entity, funds-handling arrangements, screening responsibilities, and escalation path.
- Document country-data requirements. Specify required fields, validation rules, and ownership of requirement updates.
- Define monetary authorization. State which changes to recipient details, fees, FX, or funding trigger reapproval.
- Agree status semantics. Record exactly what submitted, accepted, credited, rejected, and returned mean.
- Test ambiguous outcomes. Include timeouts, duplicate requests, delayed notifications, partial batch execution, and returns.
- Reconcile the whole cycle. Demonstrate that principal, conversion, charges, and refunds connect back to the source obligation.
- Preserve portability. Confirm that recipient records, transaction histories, and audit evidence can be exported under applicable privacy requirements.
Choose connected control, not another payment silo
A global payout platform earns its place when finance can follow an obligation from approval through funding and delivery to the ledger—without losing ownership at provider handoffs.
Payouts.com's financial operating system brings global payouts, treasury, AP/AR automation, and AI digital employees onto one ledger. The financial OS approach treats payment execution as part of the company's wider money cycle, rather than an isolated endpoint.
Start by mapping one representative payout cycle, including an exception, against the ownership table above. Then explore Payouts.com payout automation against those requirements. The goal is not merely fewer interfaces; it is fewer gaps between authorizing money and accounting for where it went.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
36 commentsRelated resources
One Platform for Your Team and Your AI Agents: Inside the Financial OS
The shape of a finance team is changing. Here's how one platform runs global payouts, AP, AR, cards, and compliance on a single ledger — for humans and AI agents alike.
Klarna Launches Stablecoin to Cut Cost of Cross-Border Payments
KlarnaUSD signals a move toward stablecoins inside payment providers’ settlement infrastructure. For finance teams, the opportunity depends on end-to-end economics—not just cheaper blockchain transfers.
How Does eBay Pay Sellers? Methods, Deductions, and Net Proceeds
eBay collects buyer payments and pays sellers their net proceeds through supported payout destinations. Here is how account setup, deductions, currency conversion, and reconciliation fit together.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The point about preserving source obligation ID, payment instruction ID, and execution attempt ID separately is something we had to learn the hard way. Our first platform treated everything as a single transaction record and when we had failures or partial refunds months later, we couldn't trace back to the original AP invoice without manual detective work.
We went through the same thing. The problem got worse when returns came back 45+ days later and we had already closed the period. Now we enforce a rule that the obligation ID lives in the ERP and never changes, even if we retry through a different route or provider.
We went through the same thing. The problem got worse when returns came back 45+ days later and we had no way to link them to the original AP record because everything had been flattened into one transaction ID. Now we enforce separate IDs at each stage and require the platform to maintain all relationships in both directions.
The part about keeping one payment identity across the money cycle is where most implementations fall apart. We had a vendor tell us their idempotency key only persisted for 24 hours, which meant a Friday timeout could theoretically become a duplicate on Monday if someone resubmitted the file.
We ran into the same thing and ended up maintaining our own idempotency layer in the middleware that wraps the provider API. The key gets hashed from source obligation ID plus recipient plus amount, and we keep it indefinitely. It's extra work but it's the only way to be sure a retry doesn't duplicate.
We ran into the same thing and ended up maintaining our own idempotency layer in the middleware. The provider's submission ID gets stored alongside our internal payment request ID with no expiration, so retries always check our table first before hitting their API.
The claim that a global payout platform should preserve ledger relationships for funding movements, conversion entries, fees, returns, and adjustments is correct in theory but I haven't seen a single vendor do this comprehensively out of the box. Most give you the principal transaction and maybe fees, but reconstructing FX gain/loss or handling a return that spans fiscal periods still requires custom work on our side.
Same experience here. We ended up building our own wrapper that links the provider transaction ID to our GL entries for FX gains/losses and fees, but returns still break the chain if they come back in a different period. The article's point about preserving ledger relationships across the entire cycle is the right architecture, but you're right that nobody ships it complete.
Agreed. We get the payment record and a separate fee line item, but FX conversions show up as a net amount with the rate buried in metadata. Returns are the worst—they come back as a new transaction with a reference to the original, but there's no automated ledger reversal. We have to manually unwind the accounting entry every time.
The responsibility map table is good but I wish it went further on who owns the actual compliance decisions when a payment gets flagged. We have a platform that surfaces sanctions hits and route restrictions, but the vendor still expects us to make the final call on whether to proceed or reject. That decision authority needs to be explicit in the contract, not just the workflow.
We ended up documenting this explicitly in the vendor contract addendum. If their screening engine flags it but doesn't auto-block, we own the decision and they document our instruction. If it's a regulatory hard stop in their license jurisdiction, they own the block. The gray area is reputational risk flags where neither party wants final accountability.
We ran into the same ambiguity. Our vendor's compliance team screens transactions but won't make business decisions on borderline cases. We ended up creating an internal decision tree for common flag types and assigning a specific person in finance ops to own escalations. The platform should at least document what evidence they used to flag it so you're not making the call blind.
The point about a positive balance not meaning a payment can execute is something we learned the hard way. We had 'available funds' that were actually in the wrong currency or locked in a sub-ledger that required a manual sweep. Now we make the platform show executable balance by route, not just total.
We built a similar view after getting burned on FX quotes that expired before we could actually execute. Now the platform shows not just currency balance but also quote validity window and whether the recipient is fully validated for that specific rail. Turns out 'executable' has about five prerequisites that most dashboards don't surface.
Exactly this. We now require the platform to return executable balance per route and currency pair before we even show the payment option to the user. Saved us from a lot of failed attempts and support tickets.
The division between 'executable payment' and 'delivery evidence' is something we should have clarified with our provider two years ago. We were treating provider confirmation as final settlement and got burned when beneficiary banks rejected or reversed credits days later, but our ERP had already closed the liability.
We finally added a reconciliation step that requires both the provider's completed status and a separate settlement confirmation before we mark the payable as discharged in our system. It added two days to our close process but stopped the reversals from breaking our monthly accruals.
We had the same issue. The problem was our provider's API returned 'completed' once they submitted to the beneficiary bank, not when funds were actually credited. We ended up adding a 72-hour hold before marking obligations discharged in our subledger, which helped but created its own reconciliation headaches at month-end.
The section on separating rail access from delivery promise is critical but I think it undersells the operational chaos. We have one provider that marks payments 'completed' when they leave their ledger, another when funds hit the correspondent, and a third only after beneficiary credit. Trying to explain to business owners why three successful USD-to-MXN payments have three different timelines has been a nightmare.
We deal with this every month-end close. The only thing that worked was forcing providers to send us both their internal status and the actual downstream network confirmation code. Now we map those codes ourselves and ignore their summary labels entirely.
We deal with this every month-end close. The only thing that worked was forcing providers to surface both their internal status and the raw network response code, then we map those ourselves in our middleware. Still not perfect but at least the reconciliation team knows what they're looking at.
The responsibility map is useful but it assumes your platform vendor will actually let you retain control over things like beneficiary authorization and accounting treatment. In practice we've found that many vendors want to own the entire flow and push back hard when you try to keep approval logic in your ERP or treasury system.
We had the same pushback during vendor selection. What worked was being explicit in the RFP that approval workflow and GL mapping had to remain in our ERP, and the platform would only execute what we authorized. About half the vendors dropped out immediately, which actually saved us time.
This is exactly why we walked away from two vendors before finding one that would expose approval hooks via API. The article's point about documenting who defines limits versus who applies them helped us structure the RFP differently the third time around.
The section on country-specific requirements is helpful but in practice we've found that even the same country can have different field requirements depending on which local bank the provider partners with. India is especially messy—some routes need additional purpose codes that others don't, and the error messages rarely tell you which field is actually wrong until you've already submitted.
We hit this with our India payouts too. The article's point about distinguishing available route from executable payment helped us clarify internally which field mismatches were actual blockers versus just provider UI confusion. Still painful though.
This is exactly right. We see the same with Brazil—some providers require tax ID at the beneficiary level, others only for certain transaction types or amounts. The article's point about platforms serving current field requirements for the selected route is key, but in reality most platforms just show you the superset of all possible fields and let you figure out which ones actually matter for your specific provider-destination combination.
The ownership map table is the most useful thing I've seen on this topic in a while. We had exactly this problem—AP approved invoices, treasury managed FX, and the platform just tracked submission status. Nobody owned exceptions end-to-end and we were reconciling failures in Slack threads.
We solved this by making treasury the single owner of exception resolution, but gave them a dashboard that pulled from AP, the platform, and banking APIs. Still not perfect but at least failures don't sit in limbo while teams point fingers.
Same here. We finally assigned each layer to a specific Slack channel with a documented owner—AP owns payable intake, treasury owns funding/FX, ops owns recipient data. The platform just surfaces blockers to the right channel. Took about three months to stop having the same failure investigated by four different people.
"A status called 'completed' is useful only if its meaning is documented." This drove me crazy at my last company. Our provider marked payments complete when they left their system, not when the beneficiary was credited. Finance reported the liability as settled, then we'd get inquiries weeks later from contractors who never received funds.
We had the exact same problem and ended up requiring two statuses in our reports: provider accepted and beneficiary confirmed. The second one often comes days later depending on the rail, but at least AP knows not to close the period until we have actual proof of credit.
We ended up building a reconciliation layer that requires both the provider confirmation AND a bank statement match before the AP system gets the completion signal. It's slower but we stopped having to reverse closed periods.
Curious how people are handling the stable business reference requirement when payments span multiple systems. We generate IDs in NetSuite but sometimes ops teams retry failed payments directly in the payout platform, which creates orphaned records that reconciliation picks up months later.
We enforced a rule that only NetSuite can create the source obligation ID, and the payout platform treats it as immutable. Retries use the same reference but increment the execution attempt counter. Took some workflow changes but reconciliation became way cleaner.
We had the same issue until we locked down manual retries. Now if a payment fails, the platform writes the failure reason back to the ERP and ops has to resubmit from there with the same reference. Takes longer but reconciliation actually closes now.