

Accounts Payable Fraud Prevention Controls That Survive Payment Release
An approved invoice can still become a fraudulent payment. Build controls that preserve authorization from vendor setup through bank release—and test whether your AP software actually enforces them.
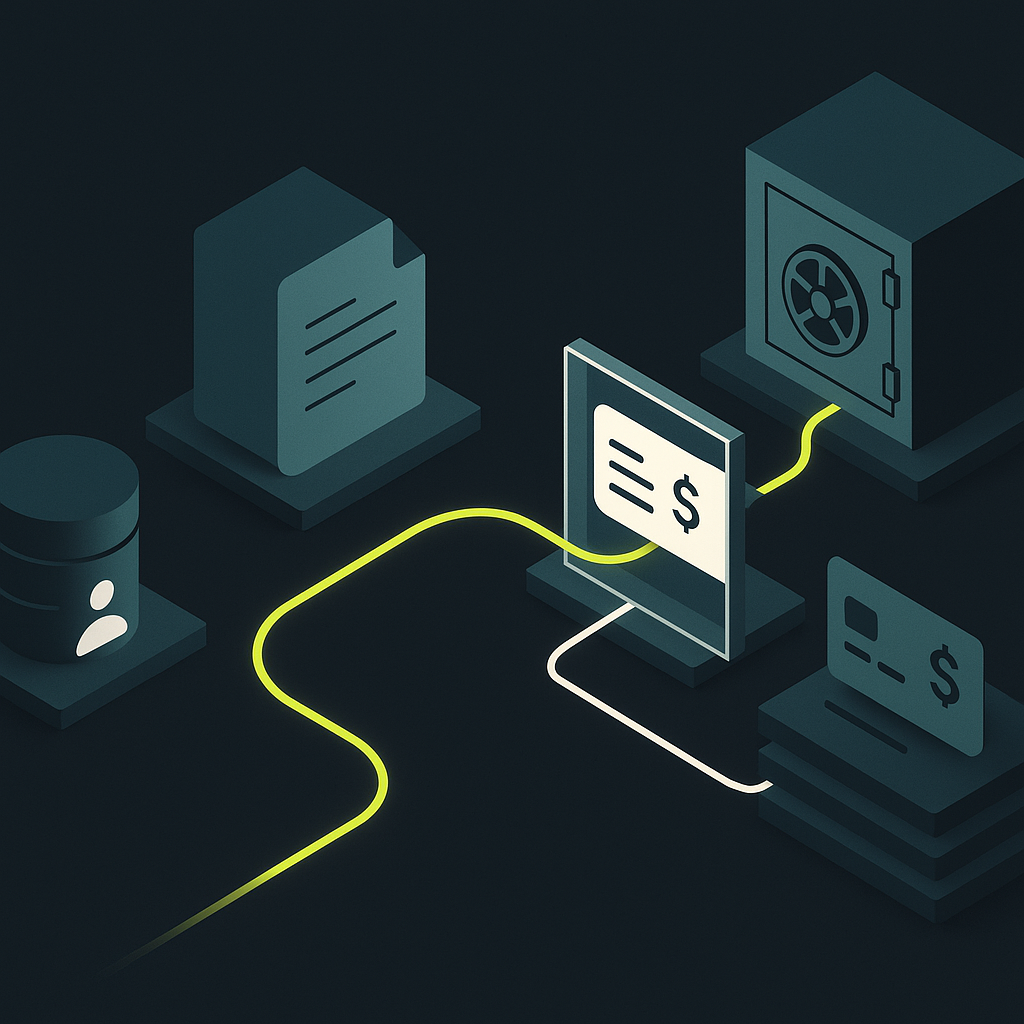
Effective accounts payable fraud prevention controls combine independently verified vendor details, segregation of duties, invoice validation, enforced approvals, protected payment release, and independent reconciliation. The critical requirement is continuity: approval must remain tied to the supplier, destination account, amount, and currency that were authorized. Material changes should stop payment and trigger the appropriate verification and reapproval.
For finance teams moving from email approvals and bank portals to automation, this is the buying question: does the platform enforce that continuity, or simply move invoices faster?
The 2025 AFP Payments Fraud and Control Survey found that 79% of respondent organizations experienced attempted or actual payments fraud in 2024. That covers payments broadly, not AP alone, but reinforces why invoice approval cannot be the final fraud checkpoint.
Start with the handoffs, not the feature list
Fraud controls often fail between systems. AP approves an invoice in one application, treasury exports a payment file, and an operator uploads it to a bank portal. Meanwhile, someone updates the vendor master. Each system may show an authorized action without proving that the final payment matches the original authorization.
Map every place a person, integration, or service account can change the payee, destination, amount, currency, or payment status. Then identify which changes invalidate approval and which system blocks release.
Use the following matrix as a control-design baseline. These are recommended requirements to validate, not claims about any particular product.
| Risk point | Preventive control | Accountable owner | Evidence to retain |
|---|---|---|---|
| Fictitious vendor | Independent supplier verification | Vendor master owner | Identity checks and business sponsor |
| Bank-detail substitution | Trusted-channel verification and separate approval | Vendor master approver | Change history and verification record |
| Unsupported invoice | Matching or documented service acceptance | Business budget owner | Order, receipt, or acceptance evidence |
| Self-authorized payment | Conflicting-role restrictions | Controller | Permissions and approval history |
| Post-approval alteration | Hold and reapproval for material changes | Payment approver | Approved and released payment versions |
| Bank-portal bypass | Restricted access and independent release | Treasury lead | Bank authorization record |
| Concealed disbursement | Independent reconciliation and investigation | Accounting reviewer | Resolved exceptions and bank records |
Verify vendors and protect payment-detail changes
A legitimate invoice does not prove that the bank account printed on it belongs to the supplier. Neither does a reply from a familiar email address: the supplier's mailbox may be compromised.
Commerce Bank's AP fraud guidance emphasizes separating responsibilities and independently confirming changes to payment information. Turn those principles into a mandatory workflow:
- Establish a trusted baseline. Verify the supplier's identity, business purpose, and authorized contacts before enabling payment. A tax document alone does not establish account ownership.
- Quarantine requested changes. Store proposed bank details separately from the currently approved record. Do not overwrite the active destination on receipt of an email.
- Verify through an established channel. Contact a previously validated supplier representative using contact details not supplied in the change request. Record who verified the request and how.
- Require independent approval. The person entering the change should not approve their own modification.
- Reassess pending payments. Hold affected instructions until the new destination is verified and the appropriate payment authorization is renewed.
Where available, account-name or ownership checks can provide additional evidence. Coverage and match quality vary by market and provider; treat inconclusive results as exceptions, not successful verification.
A portal also needs controls. Strong authentication, protected contact changes, and recovery procedures matter because a compromised supplier account can submit a fraudulent request through a legitimate interface.
Separate authority across the full payment chain
Segregation of duties means more than having different people capture and approve invoices. Review who can create suppliers, edit bank details, approve invoices, release payments, administer permissions, and reconcile bank activity.
The AP internal controls framework described by Ramp includes segregation of duties and invoice matching. The operational challenge is enforcing those controls across applications, not just within AP.
For example, a clerk restricted from releasing payments in the AP platform may still have unrestricted bank-portal access. An administrator may be able to grant themselves approval rights. A shared integration credential may bypass restrictions applied to human users.
- Use named identities and strong authentication for finance and bank access.
- Review conflicting permissions across the ERP, AP platform, bank, and integration layer.
- Log privileged access changes and have someone independent review them.
- Apply equivalent restrictions to service accounts and AI agents.
- Make temporary delegation expire and prohibit self-approval through delegation.
Small teams may need compensating controls, such as independent owner approval of new beneficiaries and direct review of bank activity. Document the remaining concentration of authority: a detective review after settlement is not equivalent to a preventive release block.
Validate the obligation without trusting appearances
For purchase-order-backed goods, match the invoice to the approved order and receiving evidence. Configure tolerances deliberately, and route discrepancies to an accountable owner rather than automatically accepting them to improve processing rates.
Services and non-PO spending need a different evidence path: an executed agreement, milestone acceptance, or documented confirmation from the business owner that the service was delivered. Coding an invoice to an expense account is not proof of performance.
Duplicate checks and anomaly detection help identify suspicious submissions, but alerts require ownership and resolution. Conversely, a clean match is not a guarantee against collusion: coordinated purchase orders, receipts, and invoices can agree while describing a fictitious transaction.
Keep invoice extraction separate from vendor-master authority. OCR or an AI agent may capture bank details from a document; that should not authorize those details to replace the approved beneficiary.
Bind approval to what actually leaves the bank
Configurable approval policies should address more than spending thresholds. Define which changes invalidate existing authorization, including supplier substitution, beneficiary changes, increased amounts, and currency changes.
Hypothetical example: A genuine supplier invoice is approved for payment. Before the payment run, an attacker sends new bank details from the supplier's compromised mailbox. The invoice remains valid, but the destination is now untrusted. A robust workflow holds the affected payment, verifies the change independently, and obtains authorization for the revised instruction.
Ask vendors to demonstrate this sequence. Can they show exactly which beneficiary record the approver authorized? What happens if an API updates that record after approval? Does a queued payment retain the old destination, adopt the new one, or stop?
For file-based bank uploads, restrict file editing and reconcile released instructions to approved instructions. Batch totals alone are insufficient: a substituted beneficiary can leave the total unchanged.
Emergency payments need an exception path with a named approver, documented reason, and preserved verification requirements. Executive urgency should not become an informal bypass.
Use reconciliation to detect failure—and prepare to respond
Reconciliation is detective, not preventive. Independently compare bank activity with authorized payments, investigate unexpected beneficiaries and manual disbursements, and track unresolved exceptions to closure.
Retain a connected audit trail: source invoice, matching evidence, vendor-record history, approver identity, policy applied, overrides, payment instruction, and bank reference. Confirm who can alter or delete those records.
If suspected fraud is discovered, contact the financial institution immediately to request available recall or recovery measures, stop pending related payments, preserve evidence, and involve security and legal teams as appropriate. Recovery depends on the payment rail, timing, and circumstances; do not assume it is possible.
A buyer's checklist for the product demonstration
Ask each shortlisted provider to demonstrate failure cases, not only a clean invoice-to-pay flow:
- Change a beneficiary after approval: Does release stop, and what evidence unlocks it?
- Attempt self-approval: Do delegation, administrator access, and API credentials preserve role separation?
- Submit an unsupported invoice: Is missing receipt or service evidence routed to a named owner?
- Alter a payment export: Can the team detect a changed destination despite unchanged batch totals?
- Request an urgent override: Are authorization, rationale, and verification retained?
- Reconstruct a payment: Can an auditor trace the released instruction back to its approval and vendor-record version?
Track unresolved exceptions, unverified bank changes, overrides, and payments released outside the approved workflow. Evaluate cost per invoice alongside those measures. Lower processing cost achieved by removing necessary checks is not a control improvement.
Automate the controls before removing the touchpoints
The goal is not manual review everywhere. It is a trusted path for routine transactions and a hard stop when evidence, authority, or payment details change. That distinction is central to touchless invoice processing.
Before selecting an AP automation platform, bring your role map, bank-change procedure, and demonstration checklist. Require clarity on which controls the platform enforces, which depend on integrations or bank settings, and which remain your team's responsibility. Approval is only effective when it governs the payment that actually leaves the account.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
3 commentsRelated resources
Touchless Invoice Processing: What It Really Means and How to Get From 0% to 80%+
Touchless invoice processing isn't a switch you flip — it's a rate you climb. Here's what it really means, how to measure it, and a step-by-step path from 0% to 80%+.
Invoice Approval Workflow: Build a Matrix That Holds Up
An effective invoice approval workflow defines who can approve, what evidence they need, and when approval must reset. Use this framework to turn an email-based process into enforceable rules.
Duplicate Invoice Detection: Evaluate the Control, Not the Alert
A duplicate alert is not the same as a prevented payment. Learn how to evaluate matching accuracy, exception handling, and payment-release controls before choosing AP automation.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The handoff mapping exercise is spot on. We had a situation last year where an invoice approved in our ERP got modified during the payment file export—amount was correct but routing number had been changed in the vendor master two days after approval. No one caught it until reconciliation because each system showed green checkmarks. Now we hash critical fields at approval and validate before release.
"Does the platform enforce that continuity, or simply move invoices faster?" This should be printed on every RFP. Half the demos we sat through last quarter showed slick approval workflows but went silent when we asked what happens if someone edits the beneficiary between approval and file generation.
Question on the trusted-channel verification: how are you all handling this for international suppliers where phone contact is expensive or impractical? We've been using video calls for large changes but it doesn't scale, and some of our smaller vendors in APAC don't have consistent availability.