

Mastercard and PayPal Agentic AI Payments: The AP Gap
Mastercard and PayPal are building infrastructure for AI-initiated checkout. For finance leaders, the critical distinction is between permission to transact and approval to spend company money.
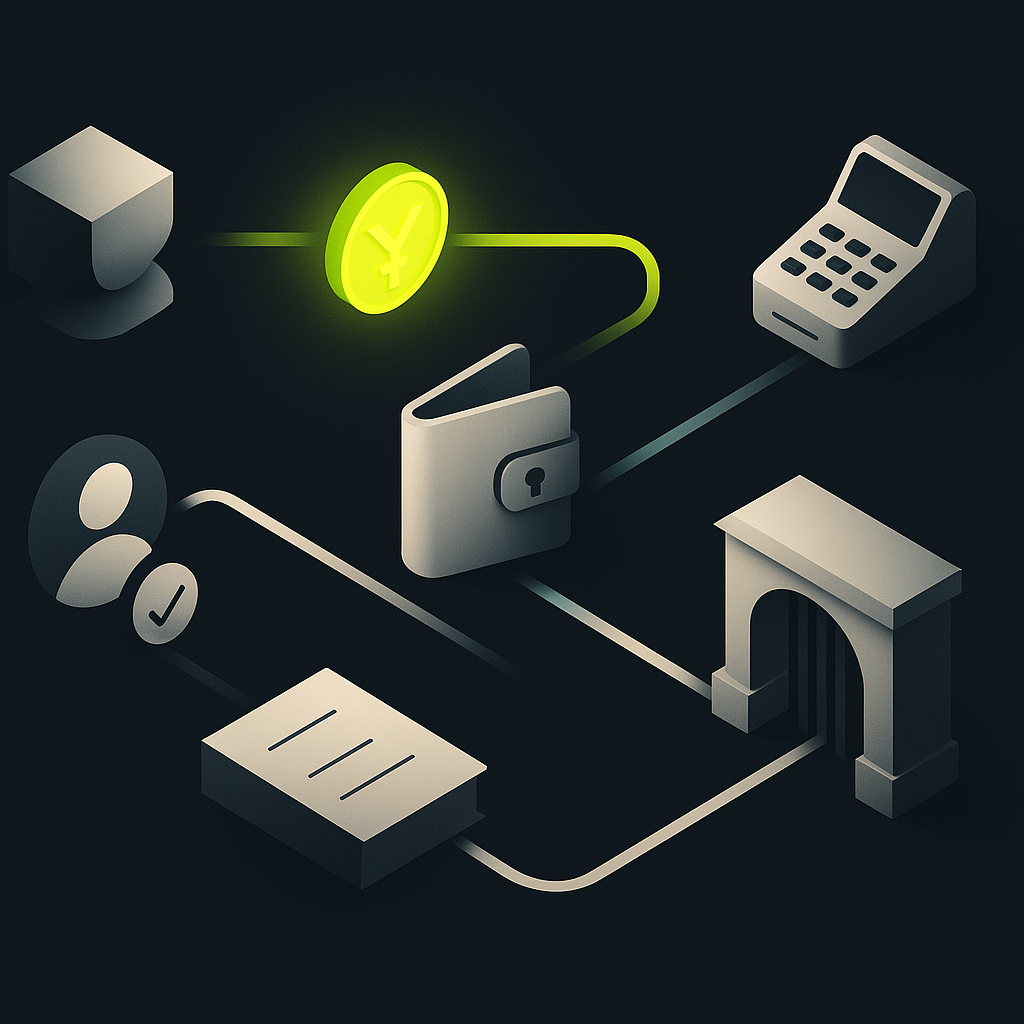
Mastercard and PayPal’s agentic AI payments partnership is designed to let AI agents transact on behalf of PayPal users through Mastercard Agent Pay. It addresses payment credentials, authentication, and acceptance—not the entire accounts payable process. A securely authenticated purchase can still violate a company’s procurement policy, duplicate an invoice, or land in the wrong ledger account.
For CFOs and controllers, the practical question is therefore not simply whether an agent can pay. It is whether the company can connect that payment to an approved obligation, enforce restrictions at execution, and reconcile what happened afterward.
What Mastercard and PayPal announced
In their October 27, 2025 partnership announcement, Mastercard and PayPal outlined plans to integrate Mastercard Agent Pay into the PayPal wallet. The announcement also described PayPal piloting Mastercard’s Agent Pay Acceptance Framework to support secure acceptance of agent-initiated transactions.
The intended division of labor is straightforward: Mastercard supplies agentic payment infrastructure, while PayPal brings its wallet and merchant checkout ecosystem. Together, they aim to make delegated purchases usable within existing payment relationships.
That is not evidence that every PayPal merchant, funding source, geography, or enterprise purchasing workflow supports autonomous checkout. Finance teams should distinguish an announced integration, a pilot, and a supported production configuration. Confirm availability for the exact wallet, card, merchant, and market involved.
How the payment mechanisms work—and where they stop
Tokenization protects credentials
Mastercard’s April 2025 Agent Pay launch introduced Agentic Tokens, building on its existing tokenization infrastructure. Tokenization substitutes a payment token for the underlying card number, reducing the need to expose raw credentials within a purchasing workflow.
This matters when software, rather than a person entering card details, initiates checkout. However, protecting the credential does not establish that the purchase is commercially justified. A token cannot independently confirm that goods were received or that an invoice has not already been paid.
Authentication and acceptance establish payment trust
The partnership announcement describes tokenization and passkey authentication as components of its approach. These mechanisms help address whether payment access is legitimate and how agent-originated transactions can enter merchant acceptance flows.
For corporate spending, finance must ask a separate question: who had authority to delegate this purchase? A valid user authentication does not necessarily mean that user can approve the relevant cost center, supplier, or contract commitment.
Agent detection is not spending authorization
Later developments should also be read narrowly. Reporting on Mastercard’s September 2026 trust services describes an agent-initiation probability score entering testing in the United States. That is a signal about whether an agent initiated a transaction—not proof of company approval. The reported announcement does not establish global general availability, a performance benchmark, or a liability rule.
The distinction matters operationally: identifying an agent, authenticating payment access, and approving a business expense are different decisions. No single signal should stand in for all of them.
The responsibility map finance should build
Treat the Mastercard–PayPal arrangement as payment infrastructure within a broader control system. Before enabling a corporate use case, assign an owner and an evidence requirement to each handoff.
| Layer | Question it addresses | What finance must establish |
|---|---|---|
| Agent identity | Which agent is acting? | Accountable owner and permitted role |
| Payment credential | How is payment access protected? | Approved funding source and restrictions |
| Purchase delegation | What may the agent buy? | Scope, expiry, and change rules |
| AP approval | Does the company owe this amount? | Invoice, order, receipt, and approval evidence |
| Execution | Can this transaction proceed now? | Current limits and duplicate checks |
| Reconciliation | What actually happened? | Capture, settlement, refund, and ledger matching |
This is a responsibility map, not a claim that the partnership supplies every layer. Its value is exposing gaps between checkout security and financial accountability.
Where AP agents can act—and where humans should remain
Low-risk autonomy is most useful before money moves. Under defined policies, agents can propose invoice coding, match invoices against purchase orders and receipts, and send approved reminders for missing documents. Ambiguous coding, unmatched items, and conflicting records should enter an exception queue rather than be silently resolved.
Vendor communication needs boundaries too. An agent may request a missing invoice through an established contact channel; it should not treat a reply containing new bank details as authorization to change the vendor master.
Require human approval for new suppliers, changed payment destinations, expanded purchasing authority, and unresolved matching exceptions. Routine purchases may be eligible for delegated execution only when the company has explicitly approved that scope and the system enforces it independently of the model.
The workflow belongs in the company’s AP automation process, not solely in a conversation with an assistant. Configurable approval policies should determine when an agent may proceed and when it must stop. The agent must not be able to rewrite the rules that authorize its own spending.
Hypothetical example: an approved reorder that changes at checkout
Suppose a company authorizes an agent to reorder an approved office supply from an existing supplier. The purchase approval specifies the item, quantity, delivery location, and maximum total, including shipping and tax.
At checkout, the supplier substitutes a different item and adds recurring replenishment. The payment credential may still be valid, and the merchant may still be able to accept the transaction. Neither fact makes the revised purchase acceptable.
A defensible workflow compares the final checkout terms with the approved purchase:
- Unchanged terms: proceed only if current policy and funding checks also pass.
- Changed item or recurring commitment: stop and obtain fresh approval.
- Unclear payment response: check transaction status before retrying.
- Later refund: link the refund to the original purchase and accounting record.
The useful design principle is to preserve the approved purchase details and compare them with the executable transaction. Do not rely on the agent remembering the conversation correctly.
A checklist for evaluating the partnership in your finance stack
- Verify the supported configuration. Ask the provider to identify the applicable market, card, wallet, merchant integration, and production status. Separate roadmap statements from contractual support.
- Define the business object being approved. Specify whether approval covers an order, an invoice, a single checkout, or a recurring commitment. Record which changes invalidate it.
- Identify the enforcement point. Determine which system rejects an out-of-policy transaction. Instructions in a prompt are not a substitute for an execution control.
- Test revocation and in-flight transactions. Ask what happens when authority is withdrawn after an order starts but before payment completes. Establish what can be stopped and what requires cancellation or refund.
- Protect against duplicate obligations. Prevent an agent-paid purchase from later entering a separate invoice payment run. Link order, invoice, and payment references; apply duplicate invoice detection across those records.
- Document failure and dispute ownership. Establish who investigates an unauthorized purchase, merchant mismatch, failed capture, or missing refund. Do not assume agent verification changes liability.
- Require usable evidence. Retain the approval, agent identity, final purchase terms, payment reference, exceptions, and accounting outcome. Test whether operations can reconstruct the event without interpreting a chat transcript.
Build around the obligation, not just the checkout
Mastercard and PayPal’s partnership is an important effort to bring trusted payment access into agent-driven commerce. Its relevance to AP is real, but bounded: secure execution does not replace procurement approval, invoice validation, or reconciliation.
Payouts.com approaches the broader money cycle through a shared ledger, AP/AR automation, treasury, and AI agents with identities, wallets, and spend limits. That operating model addresses a different layer from merchant checkout; it should not be read as a claim of a Mastercard Agent Pay–PayPal integration.
The practical next step is to map one purchasing workflow from approved obligation to reconciled payment. Use the financial operating system approach for people and AI agents to identify where authority, execution, and accounting must connect. Expand autonomy only after that connection works—including when the purchase changes or the payment fails.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
32 commentsRelated resources
One Platform for Your Team and Your AI Agents: Inside the Financial OS
The shape of a finance team is changing. Here's how one platform runs global payouts, AP, AR, cards, and compliance on a single ledger — for humans and AI agents alike.
Duplicate Invoice Detection: Evaluate the Control, Not the Alert
A duplicate alert is not the same as a prevented payment. Learn how to evaluate matching accuracy, exception handling, and payment-release controls before choosing AP automation.
Online Tax Agent Portal: Connect Authority to the Ledger
A tax agent portal provides access to government tax services—not blanket authority for AI to act. Here is how finance teams can connect authorized tax work to controlled payments and reliable ledger records.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The layer table is useful but I'd add one more row: agent escalation path. When an agent encounters something outside its scope, where does it send the exception and how does it preserve context so the human approver doesn't have to reconstruct the entire workflow from scratch?
Agreed, and that escalation context needs to include not just what the agent was trying to do, but what rule or threshold it hit. Otherwise you're debugging the policy engine every time instead of just approving or rejecting the specific exception.
Good point. We're building this into our exception queue now—agent logs the full context including what it attempted, what changed, and which rule blocked it. The approver sees a diff view, not a blank ticket. Otherwise you're just creating more work.
The hypothetical example at the end is not hypothetical at all—we ran into almost exactly that scenario last quarter when an agent placed a stationery order that ended up enrolling us in a subscription we never authorized. The supplier changed terms between the approval step and execution, and because the agent had wallet access it went through. We're now requiring human confirmation on anything that touches a new vendor contract term, even if the SKU itself was pre-approved.
We had a near-miss with this when a supplier auto-upgraded shipping to next-day during checkout and the agent didn't flag it because the SKU matched. The delta was only $47 but it violated our blanket PO terms. Did you end up building a pre-execution verification step or just tightening the approval parameters?
Same here. The problem is the approval was locked at SKU and unit price, but the checkout page has all kinds of upsell logic that runs server-side. By the time we caught it we were two billing cycles in and had to involve procurement to unwind the contract.
The responsibility map in the middle of the article is solid but I think it understates the reconciliation problem. Even if you capture everything at execution, you still need to surface agent-initiated transactions differently in your close process because the usual AP trail (email thread, manual PO, signed approval) won't exist. Our controllers want a separate flag in the ERP for anything an agent touched so they can audit the delegation chain later.
Completely agree. We've been running a test with delegated PO generation and the reconciliation format is the blocker. Our ERP expects a human-stamped approval chain and the agent just logs a decision node. Month-end has to manually reconstruct intent from logs that weren't designed for audit.
Agreed. The audit trail for agent actions needs to be way more granular than typical AP workflows. We're building out a separate staging table that logs the agent's reasoning, any substitutions or changes from the original scope, and timestamp deltas between authorization and execution. Without that, you're flying blind when the auditors show up or when you need to troubleshoot a spike in unmatched payments.
The tokenization and passkey layer is basically table stakes at this point—what we're missing is a standard way to express spending authority that travels with the transaction. Right now every ERP and AP system has its own approval matrix format, so even if the agent can authenticate and pay, there's no portable proof it was authorized to commit that spend on behalf of the company.
This is the real problem. We've been asking our AP automation vendor if they can expose approval scope in a structured way that could theoretically be read by an external agent, and they basically said it's all internal business logic with no standard output format. So even if the agent authenticates perfectly, it has no way to know what it's actually allowed to do without scraping UI or guessing.
Exactly this. We're evaluating three different AP platforms right now and none of them expose spending authority in a machine-readable format that could travel with a payment token. Every approval rule lives locked inside the ERP and the agent has no way to prove delegation scope at checkout.
The distinction between 'permission to transact' and 'approval to spend' is the entire ballgame. We've been running PayPal Business for years and the credentials side works fine—it's the three-way match, contract compliance, and GL coding that actually protect the company. If an agent can authenticate but can't enforce our vendor approval process or duplicate invoice check, we've just automated a compliance gap.
Exactly right. And authentication layers like passkeys only confirm the agent is authorized to access the wallet—they don't touch policy enforcement at all. The gap between a valid token and a valid obligation is where most of the fraud and waste actually happens.
This is it. We're seeing vendors pitch agentic checkout as if it solves AP when it really just moves the authentication boundary. The policy enforcement and reconciliation layers still need to be built separately, and most of the demos we've sat through don't even acknowledge that gap.
The argument that a valid authentication doesn't equal spending authority is spot on, but I wish the article had gone deeper on how existing three-way match controls interact with these agent flows. If your ERP already enforces PO/invoice/receipt matching, does that layer effectively contain the agent, or do agents need their own parallel approval logic?
It does if the agent is forced to call the ERP approval endpoint before executing payment. The three-way match runs post-transaction in most setups, so you'd still get the payment through even if the invoice later fails matching. The containment only works if the agent can't bypass the PO check at execution time.
The handoff table is worth printing out and bringing to every vendor call. We've spent the last month trying to map exactly this—where our AP system ends and where the agent's checkout begins—and most vendors can't or won't answer which layer they actually cover.
Same issue. The worst response we got was a vendor insisting their API 'handles approval' because it returns a 200 status code. That's acceptance, not authorization. We now require them to map their endpoints to our internal approval states before we even start integration work.
We had the same problem and ended up building our own internal spec doc that forces the vendor to declare which layers from the table they handle. If they can't fill it out, we don't proceed with the pilot. Saves a lot of time.
The workflow belongs in the company's AP automation process, not solely in a conversation with an assistant—this line is the entire architecture decision in one sentence. If the agent can't query our ERP's approval status before executing, then it's just a chatbot with payment credentials and we've built nothing.
Right, and that API call needs to return not just a yes/no but the exact approval scope, amount ceiling, and expiry so the agent can't stretch the authorization. We built that into our workflow engine but most payment rails have no concept of it.
Exactly. We're seeing this in our current rollout—agent has to hit the ERP approval API before anything gets sent to checkout, and the response has to include dollar limit, cost center, and expiry. Otherwise you're just automating unauthorized spend.
I appreciate the caution around the agent detection probability score. Even if Mastercard can tell you an agent initiated the payment, that doesn't help me explain to our auditors why the purchase was approved or which budget it should hit. The checkout piece is honestly the easy part compared to tying it back to an obligation in our ERP.
Exactly. And the moment you have multiple funding sources or intercompany charges involved, knowing that an agent clicked the button tells you almost nothing about whether the entry will pass close. We're tracking approval authority by cost center and legal entity, and none of that lives in the payment layer.
Exactly. And the moment you have multiple funding sources or intercompany charges involved, that agent detection score becomes completely disconnected from who actually owns the expense. We're requiring human touchpoints at settlement for anything cross-entity until we see actual AP workflow integration, not just payment rails.
The responsibility map is exactly what we needed to see. We're piloting copilot tools for invoice processing right now and the vendor kept conflating 'the agent can authenticate' with 'the agent has approval authority.' Those are completely different control points and your table makes that obvious.
We hit the exact same issue in vendor demos. The worst part is when they show the agent 'successfully' completing a workflow that would have failed our internal audit. Authentication gets you into the system, approval gets you a PO number and a budget line. If your vendor can't explain where the second one happens, don't turn it on.
Same experience here. We had a vendor demo where they showed the agent completing a purchase end-to-end and our controller immediately flagged that nothing in the flow checked against our delegation of authority matrix or even our supplier whitelist. The authentication piece was polished but it had zero connection to our actual approval workflow.
Curious how you'd handle the office supply example if the substitution was minor—same brand, slightly different SKU because the original went EOL. Requiring human review for every product change would kill the efficiency gains, but auto-approving substitutions opens the door to scope creep. Maybe a tolerance threshold tied to item category?
We handle this with a tolerance band in the approval rule itself. If the substitution stays within the same GL account, same supplier, and the price delta is under 10%, the agent can proceed but flags it for post-transaction review. Anything outside that goes to the queue. You're right that pure human review kills the ROI, but you also can't let the model decide what counts as minor.
We solved this with a product category whitelist and a price variance threshold. If it's the same category, within 10% of the last approved unit price, and total is under the original budget, the agent can proceed and we review in batch weekly. Anything outside that goes to procurement. Not perfect but it keeps the queue manageable.