

Vendor Onboarding Process Checklist: Evidence for Every Sign-Off
A completed form is not an approved vendor. Use this checklist to define who signs off, what evidence they need, and which unresolved issues must block activation.
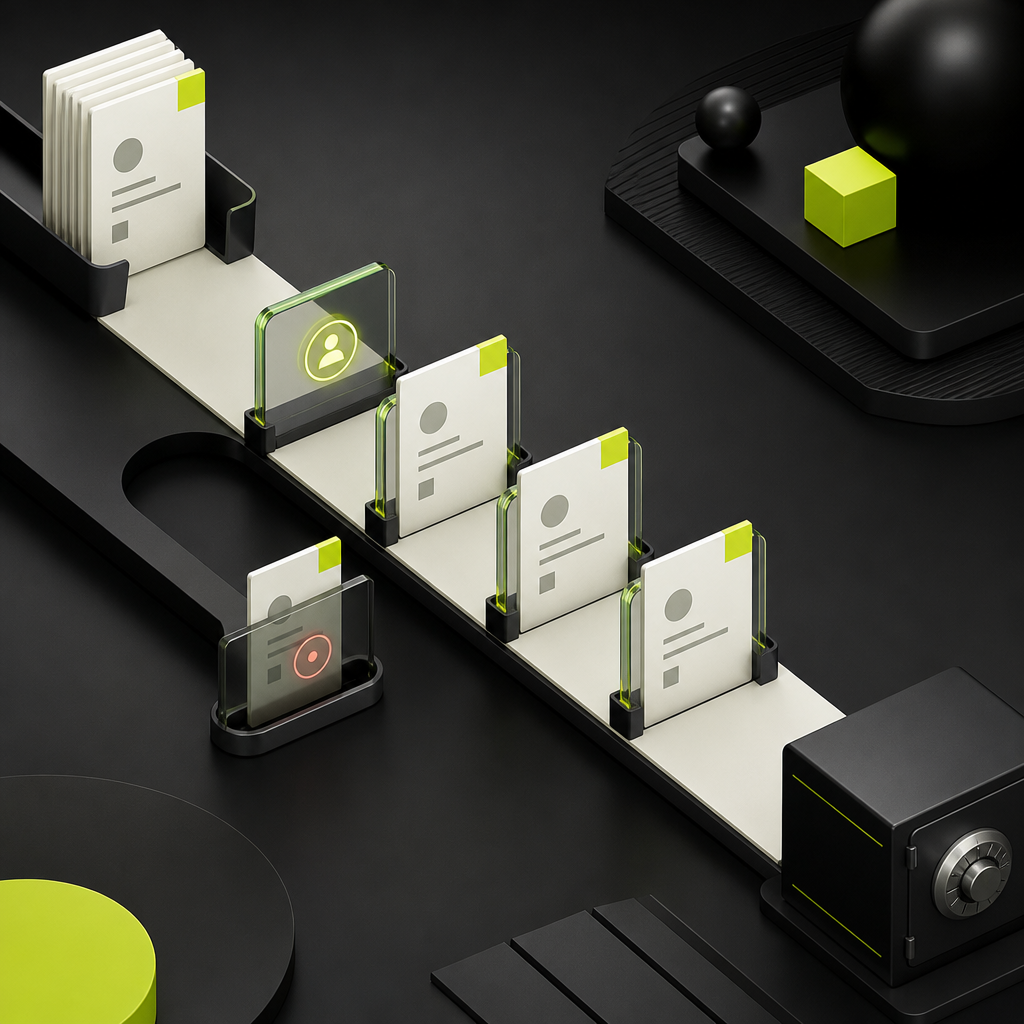
A vendor onboarding process checklist should cover the business request, duplicate checks, risk classification, identity and tax documentation, bank verification, contract terms, independent approval, and system activation. Every item needs an owner, retained evidence, and a clear rule for what happens when a check fails.
For controllers replacing email approvals and bank-portal payments, the important distinction is between information collected and permission granted. A vendor can submit every document and still be ineligible for payment. The checklist below turns onboarding into a sign-off process you can implement and test—not just a list of fields to collect.
Define what “complete” means before using the checklist
Supplier onboarding establishes the information and approvals needed to transact with a vendor. Stampli’s overview of vendor onboarding in accounts payable places this work within AP, where vendor details support subsequent invoice processing and payment.
Use explicit statuses rather than one ambiguous “onboarded” flag:
- Submitted: The vendor has provided the requested information.
- Under review: Checks are underway; unresolved items have assigned owners.
- Approved for purchasing: Commercial and risk requirements permit ordering, where policy allows.
- Payment enabled: Required payment checks are approved and reflected in the systems that release funds.
- Restricted: A change, expired requirement, or unresolved concern limits permitted activity.
These are recommended operating states, not universal regulatory categories. Configure them around your purchasing model. Crucially, creating an ERP vendor record must not automatically grant payment eligibility.
The vendor onboarding process checklist
Use this table as a working sign-off template. The owners are suggested roles; smaller teams can combine preparation tasks while preserving independent approval of sensitive actions.
| Checkpoint | Suggested owner | Evidence to retain | Completion rule |
|---|---|---|---|
| Business request | Business sponsor | Purpose, buying entity, budget owner | Need and ownership confirmed |
| Duplicate search | Vendor master administrator | Search results and disposition | Potential duplicates resolved |
| Risk classification | Procurement or risk | Tier and required review path | Applicable checks assigned |
| Identity and documents | AP onboarding | Legal details and required records | Required fields verified |
| Tax review | Tax owner or AP specialist | Applicable forms and validation result | Tax treatment established |
| Compliance review | Compliance or designated reviewer | Screening result and disposition | Relevant concerns resolved |
| Bank verification | Payments operations | Verification method, result, account version | Destination approved independently |
| Contract and invoice rules | Procurement and AP | Executed terms and invoice instructions | Commercial setup agreed |
| Activation approval | Authorized independent approver | Dated decision and evidence references | Required gates passed |
| System handoff | AP systems owner | Vendor ID and synchronization result | Receiving systems confirm correct status |
| Initial payment review | Payment approver | Approved destination and invoice linkage | No unresolved payment restriction |
For each checkpoint, record status, reviewer, decision date, evidence reference, and unresolved reason. A “not applicable” outcome should include a reason and authorizer; it should not silently count as a passed check.
Make the checks specific enough to execute
Confirm the vendor and the buying entity
Capture the vendor’s legal name, trading name, registered address, registration identifier where applicable, business contact, and remittance contact. Identify which of your legal entities will purchase and pay.
Search existing records using more than the display name. Tax identifiers, addresses, and bank-account matches can reveal duplicate records or relationships requiring review. A shared account is a review signal—not proof of wrongdoing, since legitimate group arrangements may exist.
Collect sensitive information through a controlled channel with restricted access. A self-service vendor portal can centralize submissions, but receiving a document is not the same as validating it.
Apply tax and compliance requirements proportionately
Define required documents by vendor type, location, service, and paying entity. For relevant US payer workflows, this may include Form W-9 for US persons or an appropriate W-8-series form for foreign persons. Form selection and withholding treatment depend on the circumstances; a blanket “foreign vendor equals W-8BEN” rule is insufficient.
Apply sanctions screening and other due diligence according to applicable law and your risk policy. Do not assume every ordinary supplier requires the same KYC or beneficial-ownership review as a regulated financial-services customer.
Risk tiering should consider data access, business criticality, geography, and service type—not spend alone. A low-cost software supplier with sensitive-data access may need security review that an office-supplies vendor does not.
Verify the payment destination separately
Graphite Connect’s discussion of AP risks and controls identifies vendor verification and bank-detail controls as important defenses against payment fraud. Treat banking instructions as a separate approval object, not another profile field.
- Collect account details through an authenticated, controlled workflow.
- Validate required fields for the account’s country, currency, and payment rail.
- Use an appropriate account-verification service where available; understand whether it checks format, account existence, or ownership.
- Confirm payment instructions out of band using independently established contact details, not a number supplied in the same change request.
- Require someone other than the submitter or editor to approve the destination.
A callback confirms instructions; it does not independently prove bank-account ownership. Where verification coverage is limited, document the alternative evidence and residual-risk approval rather than labeling the check “verified” without qualification.
Connect approval to invoice processing
Agree payment terms, invoice currency, purchase-order requirements, invoice submission channel, and the responsible approver. Tell the supplier which buying entity and references belong on its invoices.
This prevents onboarding from ending at record creation while AP still resolves avoidable exceptions. Reliable vendor setup supports touchless invoice processing, but vendor approval does not establish that a particular invoice is valid or that goods were received.
Add an exception register, not an email workaround
Every blocked item needs a reason, owner, next action, and review deadline. Separate incomplete submissions from failed checks: a missing certificate and an unresolved sanctions match require different responses.
Case IQ’s AP anti-fraud guidance includes separation of duties among payment controls. Apply that principle to exceptions: the person requesting urgency should not authorize their own bypass.
Define which requirements are legally mandatory, which are non-waivable policy controls, and which permit documented exceptions. For permitted exceptions, record:
- The specific requirement being deferred.
- The business reason and authorized decision-maker.
- Permitted activity, such as purchasing without payment release.
- Compensating controls and an expiry or review trigger.
Hypothetical example: A supplier is commercially approved, but its bank verification remains unresolved. If policy permits, procurement can issue an order while payment remains blocked. An urgent invoice should not convert that limited approval into unrestricted payment access.
Specify what reopens the checklist
Approval should attach to the information reviewed. A later bank-account change must invalidate the previous destination approval for that new account. A legal-entity change may require identity, tax, contract, and compliance review rather than a simple name edit.
Use change-triggered rechecks alongside scheduled reviews. Set document renewal requirements according to relevance, contractual commitments, and applicable obligations—not a universal expiry rule.
Confirm that restrictions reach downstream payment systems, including queued payments affected by a change. The broader AP fraud-prevention control framework should preserve these restrictions through payment release.
Use the checklist to test automation software
Ask providers to demonstrate the checklist with incomplete and conflicting submissions, not only a clean application. Require observable results:
- Missing evidence: The workflow identifies the missing requirement and routes it without granting payment access.
- Conflicting identity: A duplicate candidate or name mismatch remains unresolved until a reviewer records a decision.
- Changed account: Previous bank approval does not authorize the replacement destination.
- Integration failure: An unsuccessful ERP update stays visible and cannot masquerade as completed activation.
- Audit request: The system retrieves the evidence, policy decision, and approved record version.
AI can extract documents, flag missing fields, and draft follow-ups. Those tasks should not silently confer approval authority. Measure completion time by risk tier, time waiting on suppliers versus internal reviewers, exception reasons, and invoices blocked by setup defects. Avoid a single speed target that rewards premature activation.
Turn the checklist into an operating requirement
The deliverable is not a completed spreadsheet. It is a vendor record with traceable approvals, explicit permissions, and enforced restrictions.
Start by assigning an owner and evidence requirement to each checkpoint. Then use real exception patterns to evaluate Payouts.com AP Automation and the surrounding onboarding workflow. Ask how vendor readiness connects to invoice capture, approvals, and payment—and require a demonstration of what stays blocked when readiness is incomplete.
Created with AI assistance. Sources are linked in the article; this content is general information, not legal, tax, or financial advice.
Discussion
35 commentsRelated resources
Touchless Invoice Processing: What It Really Means and How to Get From 0% to 80%+
Touchless invoice processing isn't a switch you flip — it's a rate you climb. Here's what it really means, how to measure it, and a step-by-step path from 0% to 80%+.
Accounts Payable Fraud Prevention Controls That Survive Payment Release
An approved invoice can still become a fraudulent payment. Build controls that preserve authorization from vendor setup through bank release—and test whether your AP software actually enforces them.
Zimbabwe Supplier Payments in ZiG: An AP Control Guide
Zimbabwe’s ZiG supplier-payment directive concerns government procurement—not every private-sector invoice. Finance teams need transaction-level currency rules, funding checks, and settlement evidence before automating payment release.
Run your entire money cycle on one ledger
Global payouts, AP/AR automation, and AI agents with their own wallets and spend limits.
Get started
The recommendation to use search beyond display name for duplicate checks is something we learned the hard way after accidentally creating three separate vendor records for subsidiaries that all used the same remittance account. Now we flag any bank account match for manual review before the record goes active, even if the legal names don't match.
We added the same control after finding duplicate records for a vendor that changed ownership but kept the same bank details. The article's point about shared accounts being a review signal rather than proof of wrongdoing is important—we initially blocked all matches until realizing legitimate parent/subsidiary arrangements were getting caught.
The guidance on tax forms is appreciated but needs more specificity. We're stuck in a loop with procurement treating 'foreign vendor' as automatic W-8BEN requirement, but our cross-border software subscriptions involve entities that should be on W-8BEN-E or may not require withholding at all depending on treaty position. Has anyone documented decision trees for form selection that actually work for non-tax specialists doing intake?
We ran into the same procurement bottleneck. The article's point about defining tax requirements by vendor type and location is the right principle, but implementing it means your workflow needs to route to someone who can actually make that determination. We had to give tax a veto gate separate from procurement's commercial approval, which slowed things down initially but stopped the blanket W-8BEN nonsense.
We had this exact problem. What worked was building a decision tree in the onboarding workflow that asks whether the vendor is an entity or individual, and if entity whether they're claiming treaty benefits. That routes to the correct form before procurement sees it. Still requires manual review for edge cases but it stopped the blanket W-8BEN default.
The recommendation to separate collection from approval is the key insight here. We've been fighting a pattern where submitting a W-9 automatically flags the vendor as 'compliant' in NetSuite, but nobody actually validates the TIN or checks for name mismatches until the first 1099 season. By then we're chasing down amendments for dozens of vendors.
We hit the exact same thing. Ended up building a separate validation step that blocks the vendor status from flipping to 'Payment enabled' until AP confirms TIN validation through IRES or match-name-control. The real lesson was realizing that collecting the form and validating the information are two totally different controls.
We had the same pattern. The fix that actually stuck was splitting write access from approval rights in the vendor master, then running a quarterly reconciliation between vendor records flagged as tax-compliant and actual TIN validation results from our tax engine. Found about 18% mismatch rate in the first pass.
The point about ERP vendor record creation not automatically granting payment eligibility is something we're still fighting. Our NetSuite instance defaults new vendor records to payment-enabled and requires manual flag changes to block it, which means the control depends entirely on someone remembering to flip a switch. Has anyone found an ERP that handles this separation cleanly out of the box, or is custom workflow the only real option?
We had the exact same thing. Ended up building a separate validation step that blocks the payment-enabled flag until bank verification and independent approval both clear in our workflow system. The ERP default stays as-is but nothing actually processes without the external gate passing.
We had the exact same problem. The fix that actually stuck was splitting write access from approval rights in the vendor master. Finance ops can create the record and enter details, but payment flag changes require treasury sign-off through a separate approval queue. It's an extra step but it forces the verification checkpoint instead of relying on someone remembering to disable the flag.
The recommendation to treat banking instructions as a separate approval object rather than just another profile field is critical and often overlooked. We've been burned by this exact gap where vendor master data admins could update payment details without triggering any additional controls, which led to a couple of close calls before we split the workflows entirely.
We had the same pattern. The fix that actually stuck was splitting write access from approval rights in the vendor master—data stewards can edit and queue changes, but payment fields require a separate treasury sign-off that logs evidence and contact verification separately. The article's point about callback verification not proving ownership is spot on; we layer that with micro-deposit validation for new accounts.
We had the same vulnerability until we pulled bank detail approvals out of the vendor master entirely and moved them into a payment-credentials module with separate permissions. The other critical piece was blocking the AP inbox from accepting banking changes via email or PDF—everything had to flow through the portal with dual approval before it touched the system.
The part about 'not applicable' outcomes requiring a documented reason and authorizer is something we missed for two years and it created a massive audit gap. Turned out half our vendor records had skipped compliance screening with no explanation beyond an unchecked box.
We found the same thing during our SOC 2 prep. The fix was making N/A a status that requires the same approval workflow as an actual exception, with a dropdown of pre-defined reasons instead of free text. Cut down the silent skips by about 80% in the first quarter.
We found the same thing during our SOC 2 prep. The fix was making N/A a status that requires the same approval path as a waiver—has to route to the compliance owner with a written justification. Compliance screening is now either Pass, Fail, or Documented Exception. Nothing else clears the gate.
The explicit status model (Submitted, Under review, Approved for purchasing, Payment enabled, Restricted) is the most useful part of this framework. We've been treating onboarding as binary and it causes constant confusion when procurement thinks a vendor is ready but treasury hasn't cleared the bank details yet. Mapping our current mess to these five states would make handoffs much cleaner.
We had the same issue until we made 'Payment enabled' a hard gate in our payment run script. The PR team can self-serve procurement approvals but treasury has to explicitly flip the payment flag after bank verification clears. Cut down on the back-and-forth significantly.
We hit the same wall. The shift that helped us was making the status visible to all stakeholders in one place—procurement can see that their part is done but treasury's gate is still open. Reduced the 'why can't I pay this vendor yet' emails by half.
The callback-doesn't-prove-ownership caveat at the end is critical. We had a case where a vendor's compromised email confirmed fraudulent banking details over the phone using a spoofed caller ID. Now we require either a letter on official letterhead or a portal submission plus callback, and we document which method was used in the evidence field.
We had a similar fraud attempt and now use a layered approach: portal submission is primary, but any mid-cycle bank change requires a wet signature on company letterhead sent to our lockbox address, which slows things down but has stopped every spoofing attempt since we implemented it.
We went through something similar and ended up requiring portal submission plus a signed letter from the bank itself for any change over a certain threshold. It's slower but we haven't had a fraudulent change slip through since implementing it.
The checklist structure is solid but the real friction point in my experience is getting procurement to actually wait for compliance sign-off before issuing POs. We've had vendors shipping goods while still stuck in 'Under review' status, then finance gets blamed when we can't pay them because banking details aren't verified yet.
We built a hard dependency in our ERP where the PO workflow checks vendor payment status and blocks anything except 'Payment enabled'. Procurement hated it at first but now they just escalate urgent cases and we expedite the banking verification. The key was showing them how many fraud attempts we caught in the first quarter.
We solved this by requiring a procurement ticket reference at payment release, not at PO creation. If they issue early and the vendor isn't approved when the invoice hits, procurement owns the supplier communication explaining the delay. Shifted the accountability and the behavior changed pretty quickly.
The distinction between 'Approved for purchasing' and 'Payment enabled' is something we finally implemented last year and it eliminated about 80% of the back-and-forth with procurement. We were creating vendor records too early and then scrambling when invoices showed up before bank verification was done.
We had the exact same problem. The key for us was changing who owns the vendor record creation—moved it from procurement to AP so the timing lined up with payment readiness instead of PO issuance. Procurement still initiates the request but they don't get a live vendor ID until banking clears.
Same issue here. We ended up gating ERP sync entirely until payment verification clears. The operational friction was real but better than having to lock vendors post-creation or explain to procurement why a PO can't be paid for another week.
How are teams handling the independent approval requirement for bank details in practice when you're a 12-person finance function? We can't have a separate payments ops person review every account change. Are people using dual approval workflows in the ERP or is there a lighter-weight control that still works?
We split the control: same person can do the data entry and initial verification call, but the actual activation of the payment method in the ERP requires a second approver with treasury access. It's not perfect but it keeps the segregation without needing a dedicated payments ops role.
We split the control: same person can do the data entry and initial verification call, but the actual ERP payment method flag requires a second sign-off from either the controller or whoever is covering treasury that week. It's not perfect segregation but it breaks the single-actor fraud path without needing a dedicated role.
The point about risk tiering beyond spend is underappreciated. We had a $300/month SaaS vendor get compromised and they had read access to half our AR data through an integration. Meanwhile we were doing enhanced due diligence on a $50k office furniture supplier because of an arbitrary threshold.
We're running into this now with the procurement team pushing back on tiering criteria that include data access and business criticality. They want a simple dollar threshold because it's easier to enforce. How did you build the case internally to shift the framework?
We're running into this now with the procurement team pushing back on tiering criteria that include data access. Their argument is that it slows down onboarding for low-dollar vendors, but they don't see the exposure when a vendor's OAuth scopes include write access to invoice data. Did you end up building separate workflows based on integration type?